

Category filter
Hexnode UEM Patch and Update Reports
This document serves as the reference for all reports available in the Hexnode UEM Patch and Update module within the Reports tab, detailing the purpose of each report and the granular data fields they contain. These reports are critical for vulnerability management, security auditing, and demonstrating compliance across Windows,macOS and Linux fleets.
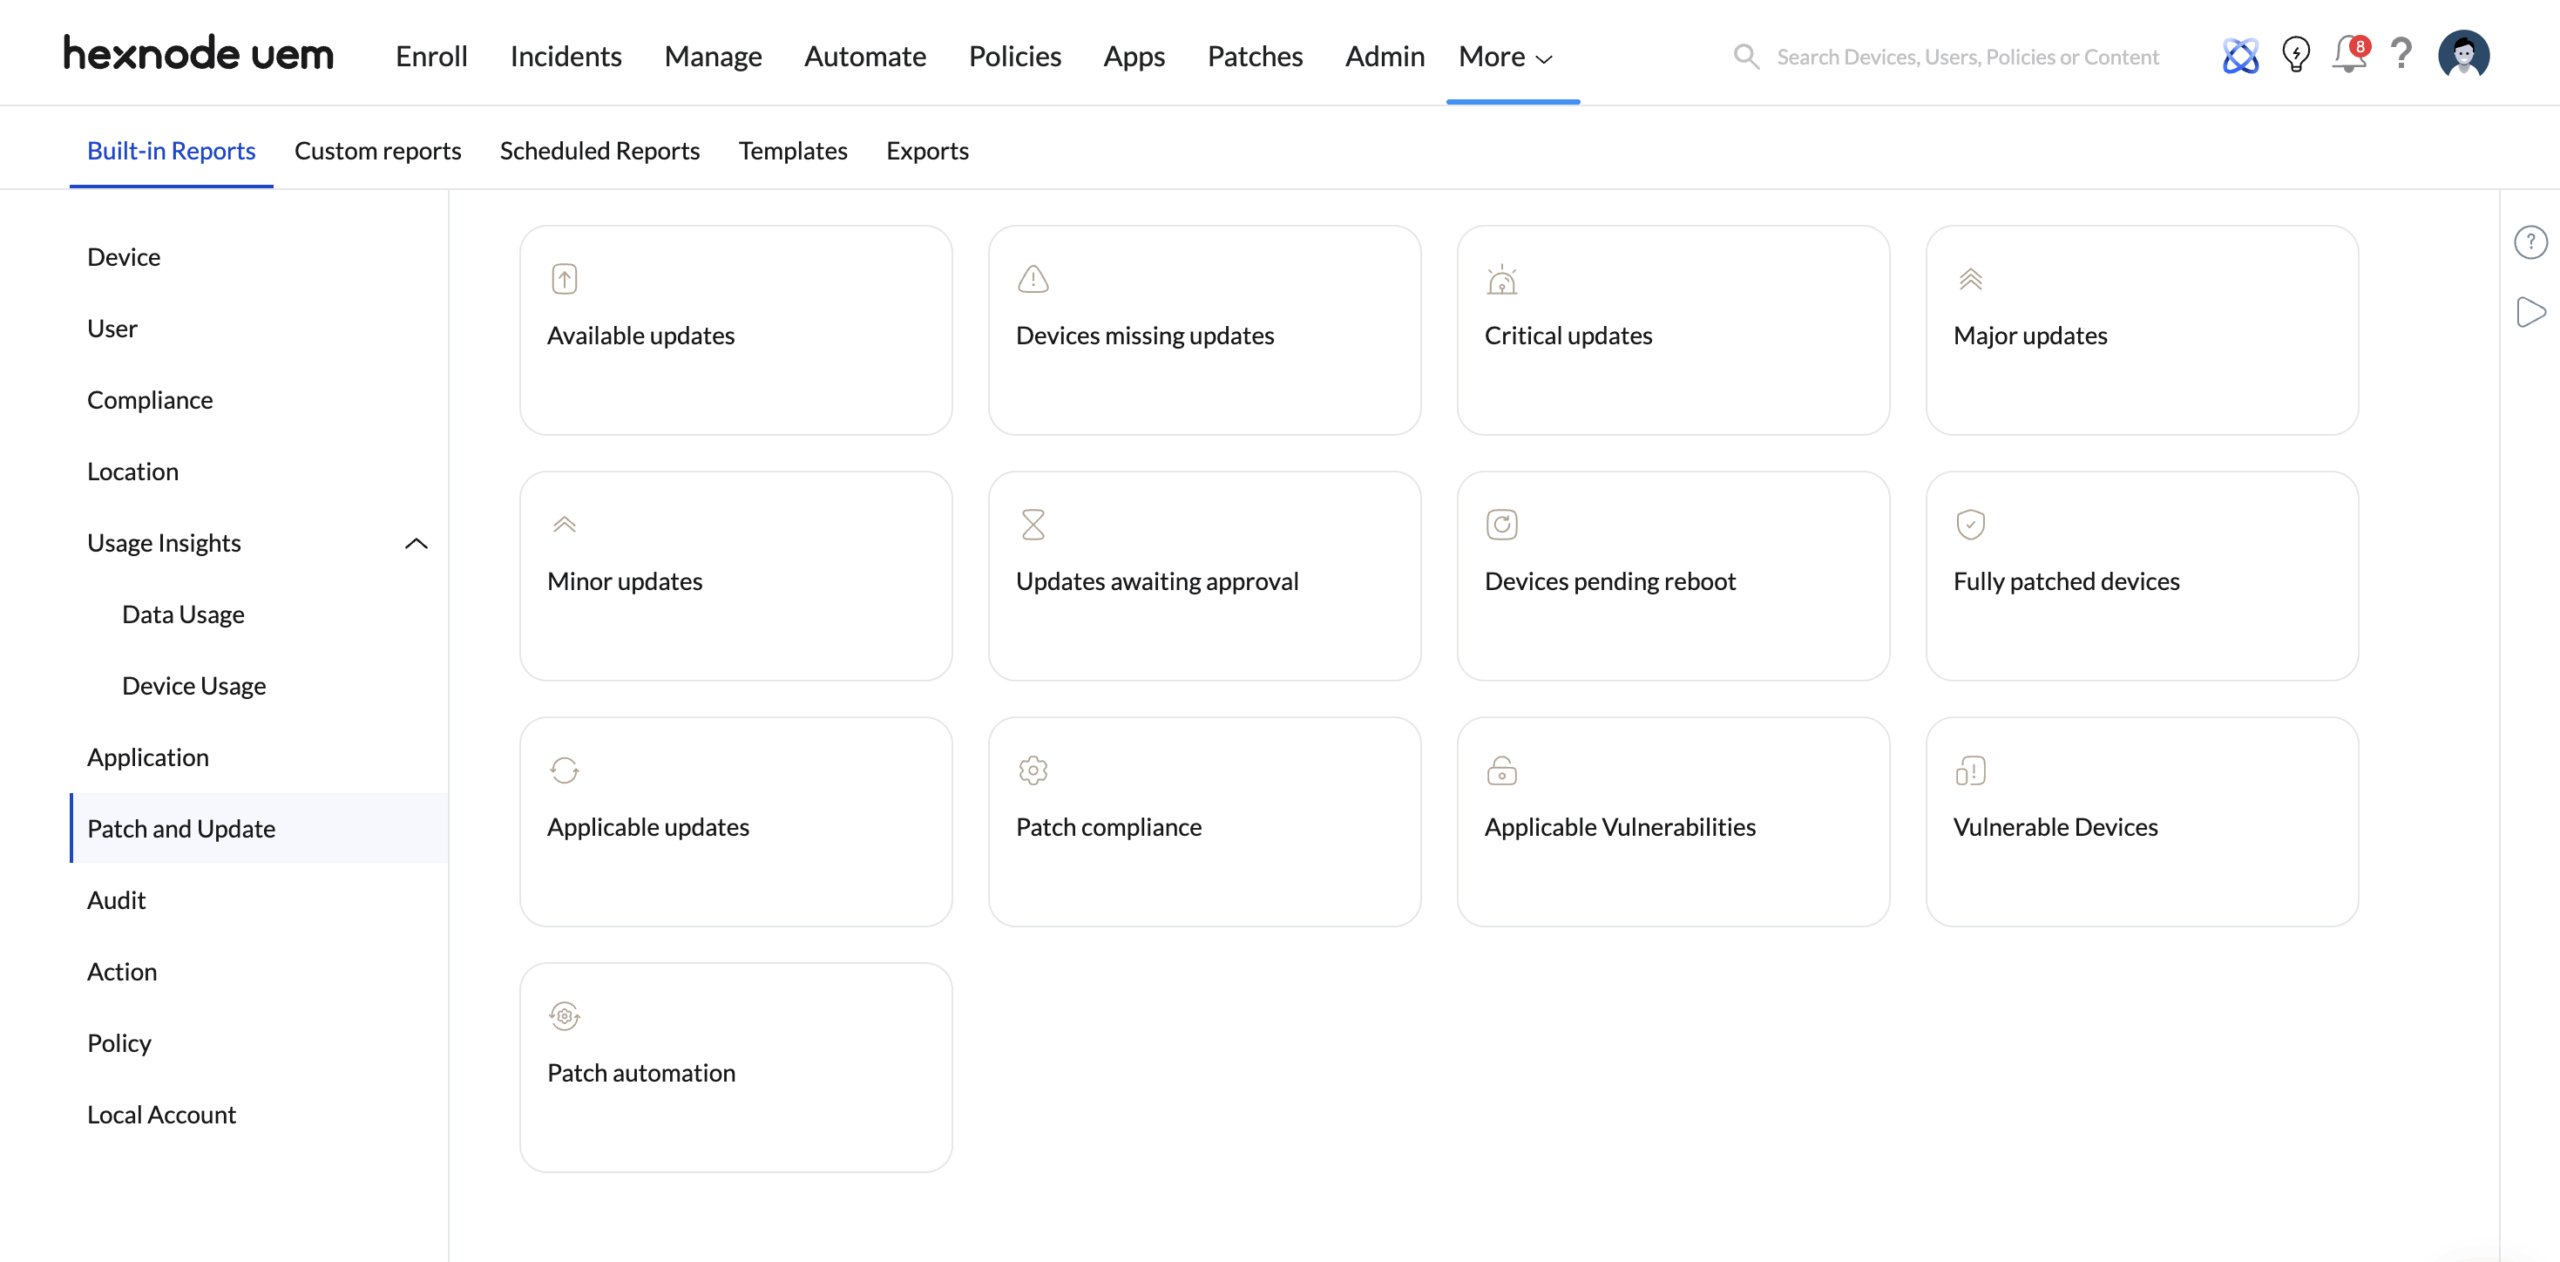
Overview of Patch and Update Reports
The Patch and Update Reports category offers the following distinct reports for auditing software status, deployment, and security posture:
Available Reports List
| Report Name | Primary Focus / Data Description | Key Data Fields Included |
|---|---|---|
| Patch Repository | A full report detailing all patches currently synchronized with the Hexnode UEM portal. | Update name, Product, Severity, Missing devices, Installed devices, Platform, Update Classification, Approval status |
| Devices missing patches | List of all devices and the updates the devices are missing. | Device Name, Username, Platform, Last Successful Scan, Missing Updates (Count with sub-report access). |
| Critical patches | List all patches with severity “Critical”. | Update Name, Description, Product, Missing Devices, Installed Devices, Platform, Release date, KB Number, Update Classification, Identifier, Type, Vendor, Max Download Size, More Information (URL), Support URL, Approval Status, Max Install Size, Beta Update, Last Update Date, Reboot, Uninstallation, Impact, Requires Network Connectivity, Requires User Input, CVSS v3.1, Applicable Devices. |
| Major patches | List all patches with severity “Important”. | Update Name, Description, Product, Missing Devices, Installed Devices, Platform, Release date, KB Number, Update Classification, Identifier, Type, Vendor, Max Download Size, More Information (URL), Support URL, Approval Status, Max Install Size, Beta Update, Last Update Date, Reboot, Uninstallation, Impact, Requires Network Connectivity, Requires User Input, CVSS v3.1, Applicable Devices. |
| Minor patches | The list of all patches with severity “Moderate”. | Update Name, Description, Product, Missing Devices, Installed Devices, Platform, Release date, KB Number, Update Classification, Identifier, Type, Vendor, Max Download Size, More Information (URL), Support URL, Approval Status, Max Install Size, Beta Update, Last Update Date, Reboot, Uninstallation, Impact, Requires Network Connectivity, Requires User Input, CVSS v3.1, Applicable Devices. |
| Patches awaiting approval | The list of all patches that are not yet approved by the admin. | Update Name, Description, Product, Missing Devices, Installed Devices, Platform, Severity, Release date, KB Number, Update Classification, Identifier, Type, Vendor, Max download size, More information (URL), Support URL, Max Install Size, Beta Update, Last Update Date, Reboot, Uninstallation, Impact, Requires Network Connectivity, Requires User Input, CVSS v3.1, Applicable Devices. | Devices pending reboot | The list of all devices with at least one update in the status “Pending Reboot”. | Device Name, Username, Platform, Last Successful Scan, Updates Pending Reboot (Count). |
| Fully patched devices | The list of devices with all applicable updates installed. | Device Name, Platform, OS Version, Device ID, Username, Last Successful Scan, Applicable Updates (Count), Installed Updates (Count). |
| Applicable patches | The list of all patches applicable to the enrolled devices. | Name, Description, Product, Missing Devices, Installed Devices, Platform, Severity, Release date, KB Number, Update Classification, Identifier, Type, Vendor, Max download size, More information (URL), Support URL, Approval Status, Max Install Size, Beta Update, Last Update Date, Reboot, Uninstallation, Requires Network Connectivity, Requires User Input, CVSS v3.1, Applicable Devices. |
| Patch compliance | The list of all applicable patches and the percentage of devices on which the patch is installed. | Name, Description, Product, Missing Devices, Installed Devices, Platform, Severity, Release date, KB Number, Update Classification, Identifier, Type, Vendor, Max download size, More information (URL), Support URL, Approval Status, Max Install Size, Beta Update, Last Update Date, Reboot, Uninstallation, Requires Network Connectivity, Requires User Input, CVSS v3.1, Applicable Devices, Patch Compliance (Percentage). |
| Applicable Vulnerabilities | The list of all vulnerabilities applicable to the enrolled devices. | Name (Vulnerability Name), Description, CVE ID, CVSSv3.1 Base Score, CVSS Vector String, CVSS Rating, CVE.org link, Affected Devices. |
| Vulnerable Devices | The list of all devices that are vulnerable along with the list of vulnerabilities. | Device Name, Platform, Device ID, Username, Last successful Scan, Vulnerabilities (Count with list access). |
| Patch Automations | The list of all automations created for patches. | Name (Policy Name), Description, Created Time, Version, Platform, Mode (Automatic/Manual), Status (Completed/In Progress), Last Status Update. |
| Windows 11 Eligible Devices | List of all devices eligible for Windows 11 upgrade. | Device Name, Username, Device model, Activity status, Device Type, Compliance status, last checked-in time, Ineligibility Reason. |
| Windows 11 Ineligible Devices | List of all devices not eligible for Windows 11 upgrade. | Device Name, Username, Device model, Activity status, Device Type, Compliance status, last checked-in time, Ineligibility Reason. |
| Devices with failed patches | List of devices where patch deployment failed and remediation is required. | Device Name, Username, OS Version,Last successful scan,failed patches |
| Unscheduled Patches | List of all patches not added to any active automation. | Name, Platform, Severity, Update Classification, Applicable devices, Missing devices, Vulnerabilities, Approval Status |
| Deployed Patches | List of all patches deployed across enrolled devices for security and operational accountability. | Name, Platform, Severity, Update classification, Automation, Applicable Devices, Missing Devices, Installed Devices. |
| Device Patch Compliance | List of enrolled devices with their compliance status, based on the OS version set in the compliance policy. | Device Name, Username, OS Version, Compliance Status, Policy Name |
| Aged Vulnerabilities | List of overdue vulnerabilities detected over 30 days ago that remain unresolved. | CVE ID, Name, CVSSv3.1 Base Score, CVSS Rating, Affected Devices |
| Critical Vulnerabilities | List of Critical-rated vulnerabilities that could be exploited on devices. | CVE ID, Name, CVSSv3.1 Base Score, CVSS Rating, Affected Devices |
| Patch Failure Summary | List of failed software patches showing the total count of affected devices for each update, used to identify problematic patches across the fleet. | Patch Name, OS (Platform), Severity, Update Classification, Number of Devices |
| Failed Patched Installation | A list of individual device-level failure records detailing which specific endpoints failed to update. | Patch Name, OS version, Severity, Update Classification, Device Name, Failure Reason |
| Successful Patch Installation | List of all patches successfully installed on enrolled devices. | Patch Name, OS version, Severity, Update Classification, Device Name, Installed Time |
| Scheduled Patch Installation | List providing the complete inventory of all patches scheduled for deployment across enrolled devices. | Patch Name, Severity,Update Classification, Automation,Target devices,Scheduled time, Created time, Technician name |
Patch Management Reports
You can also access these reports directly by navigating to Patches > Reports in the Hexnode UEM portal. These reports offer direct, real-time visibility into deployment results and endpoint compliance, allowing administrators to assess failures and initiate immediate remediation without leaving the patch workspace.
The following reports are available under this section:
Patches
- Critical patches
- Deployed patches
- Unscheduled patches
- Missing patches
- Applicable patches
- Major patches
- Minor patches
- Patches awaiting approval
- Patch repository
Devices
- Devices with failed patches
- Devices with missing patches
- Devices pending reboot
- Fully patched devices
- Device patch compliance
- Windows 11 Eligible Devices
- Windows 11 Ineligible Devices
Vulnerabilities
- Aged vulnerabilities
- Critical vulnerabilities
- Applicable vulnerabilities
- Vulnerable devices
Automations
- Patch automations
Patch Audit
- Patch compliance
- Patch failure summary
- Failed patch installations
- Successful patch installations
- Scheduled patch installations
Detailed Data Field Definitions
The data fields are segregated into four tables to distinguish between update metadata, device status, vulnerability details, and automation audit logs.
1: Fields for Update Status and Compliance Reports
These fields track patch details and approval status, relevant to Available Updates, Critical Updates, Major Updates, Minor Updates, Updates Awaiting Approval, Applicable Updates, and Patch Compliance.
| Data Field | Description |
|---|---|
| Update Name | The formal name, version, and identifier of the update or patch. |
| Description | A summary of the patch or update, detailing its purpose, resolved issues, and any improvements. |
| Product | The software, application, or operating system component that the update applies to. |
| Missing Devices | Count of devices where the update is detected but not yet installed. |
| Installed Devices | Count of devices where the update has been successfully installed. Clicking the number provides a sub-report with device details (Name, User, OS, Version, Serial Number). |
| Platform | The device operating system (OS) to which the update is applicable. |
| Severity | The criticality of the update, categorized into levels such as Critical, Important, Moderate, or Low. |
| Release date | The date when the patch or update was officially released by the vendor. |
| KB Number | The Knowledge Base (KB) reference number provided by vendors (e.g., Microsoft) for documentation. |
| Update Classification | The specific type of update (e.g., Critical Updates, Security Updates, Rapid Security Responses, Major Updates). |
| Identifier | A unique, generic identifier for the update used for tracking purposes. |
| Type | Indicates whether the update targets the OS or a specific Application. |
| Vendor | Specifies the vendor that released the update (e.g., Microsoft, Apple). |
| Max download size | Shows the maximum size of the update or patch, used for network planning. |
| More information (URL) | Provides a URL linking to a webpage with additional details or documentation related to the patch. |
| Support URL | Links to the vendor’s support page for troubleshooting or assistance regarding the update. |
| Approval Status | Indicates whether the update has been explicitly approved for installation through Hexnode UEM (Pending or Approved). |
| Max Install Size | Specifies the maximum install size. |
| Last Update Date | The most recent date when the update was added, detected, or released. |
| Reboot (Yes/No) | Specifies whether the update requires a system reboot to complete the installation. |
| Uninstallation (Yes/No) | Indicates whether the update can be uninstalled from the device after installation. |
| Impact | Displays the potential impact level of the update, categorized as Critical, High, Moderate, or Low. |
| Requires Network Connectivity | Indicates whether an active network connection is required to download, install, or uninstall the update. |
| Requires User Input | Specifies if the installation requires user interaction, such as providing consent or other inputs. |
| CVSS v3.1 | Displays the Common Vulnerability Scoring System (CVSS) v3.1 score assigned to the update. |
| Applicable Devices | The number of devices where the update status is anything other than ‘Installed’. Clicking the number provides a sub-report with device details and update status. |
| Patch Compliance (Percentage) | Displays the percentage of devices in which a particular patch or update has been successfully installed. |
2: Fields for Device-Centric Deployment Status Reports
These fields track the real-time status of individual devices: Vulnerable Devices, Fully Patched Devices, Devices Pending Reboot, and Devices Missing Updates.
| Data Field | Description |
|---|---|
| Device Name | The name of the device being reported on. |
| Username | The name of the user assigned to the device. |
| Platform | The device operating system (OS). |
| Last Successful Scan | The date and time when the device was last successfully scanned for updates or vulnerabilities. |
| Missing Updates (Count) | The number of available updates that are not installed on the device. Clicking the number provides details of the missing updates. |
| Updates Pending Reboot (Count) | The number of updates awaiting a reboot to be fully applied to the device. |
| Vulnerabilities (Count) | The number of vulnerabilities detected on the respective device. |
| OS Version | The operating system version of the device. |
| Device ID | The unique identifier assigned to the device upon its enrollment in Hexnode UEM. |
| Applicable Updates (Count) | The count of patches applicable to the device (used in Fully Patched Devices report). |
| Installed Updates (Count) | The count of patches successfully installed on the device (used in Fully Patched Devices report). |
3: Fields for Vulnerability Analysis Reports
These fields are dedicated to high-level security analysis: Applicable Vulnerabilities and Vulnerable Devices.
| Data Field | Description |
|---|---|
| Name | The formal name of the vulnerability. |
| Description | A summary of the vulnerability. |
| CVE ID | The unique identifier assigned by the Common Vulnerabilities and Exposures (CVE) system. |
| CVSSv3.1 Base Score | The base score of the vulnerability as per the CVSS version 3.1 standards, representing its severity. |
| CVSS Vector String | The CVSS v3.1 vector string describing the specific metrics used to calculate the base score. |
| CVSS Rating | The qualitative severity rating of the vulnerability (e.g., Critical, High, Medium, or Low). |
| CVE.org link | A direct URL link to the CVE.org page for more details about the vulnerability. |
| Affected Devices | List of all devices that are currently affected by the corresponding vulnerability. |
4: Fields for Patch Automation Audit Reports
These fields are specific to auditing the operational efficiency of automated deployment policies: Patch Automation.
| Data Field | Description |
|---|---|
| Name | The formal name of the patch automation policy. |
| Description | A summary of the patch automation policy, outlining its purpose or configuration details. |
| Created Time | The date and time when the patch automation policy was created. |
| Version | Indicates the version of the patch automation configuration or policy. |
| Platform | Specifies the platform (such as Windows or macOS) on which the automation is applied. |
| Mode | Displays the operational mode of the automation (e.g., Automatic or Manual). |
| Status | The current operational state of the patch automation (e.g., Completed or In Progress). |
| Last Status Update | The most recent date and time when the status of the patch automation policy was updated. |
Filters, Export, and Scheduling Options
Hexnode UEM offers flexible options for distributing and managing reports once they are generated.
Filters
Reports can be segmented by status, severity, or device group:
- Status Filter: Allows filtering results based on the patch Status (Installed, Missing, Failed, Pending).
- Severity Filter: Allows filtering results based on the reported Impact Level (Critical, Important, Low).
- Device Group Filter: Restricts the report scope to specific Custom or Dynamic Device Groups.
Export and Scheduling Options
| Action | Description | Scheduling Possibilities |
|---|---|---|
| Export | Download the report data to your local device as a PDF or CSV file. | Not applicable (Export is a manual action). |
| Schedule Reports | Configures reports to automatically run and be distributed to designated recipients. | Daily, Weekly, Monthly, or Custom Intervals. Reports are delivered automatically via email to the specified technician(s). |


