Endpoint isolation stops a compromised device from becoming a launch point for lateral movement by restricting its network access during active incident response.
Unchecked lateral movement can expand one endpoint compromise into ransomware, data exposure, wider disruption, and more complex remediation.
Isolation restricts network communication while preserving management connectivity, allowing responders to investigate and remediate the affected endpoint.
Hexnode XDR combines one-click Device Isolation with Kill Process and Quarantine File actions, supporting containment, investigation, and remediation.
Why One Compromised Endpoint Rarely Stays Contained
A compromised endpoint rarely represents the full extent of an attack. In many intrusions, the first infected device becomes a foothold for lateral movement, allowing the attacker to search for credentials, accessible systems, privileged accounts, and higher-value data elsewhere in the environment.
The initial compromise may begin with phishing, credential theft, malware execution, or exploitation of a vulnerable service. Once the attacker establishes access, the objective often shifts from maintaining control of that endpoint to expanding reach across the network.
Attackers may use stolen credentials, remote administration protocols, shared services, or trusted system relationships to access additional devices. Each successful move can bring them closer to domain-level privileges, critical servers, sensitive applications, or data repositories.
This lateral movement phase can be difficult for security teams to detect quickly. The first endpoint alert may appear limited in scope, while subsequent activity resembles legitimate administrative behavior. Authentication attempts, remote connections, and process execution can blend into normal enterprise traffic when viewed independently.
The result is a dangerous gap between detecting the initial compromise and understanding the attacker’s actual reach.
That gap creates the central containment problem. Once responders confirm that an endpoint is compromised, they must prevent the attacker from using it as a launch point for further activity.
The operational question is simple: what stops the attacker from moving to the next device before the security team can respond?
What Unchecked Lateral Movement Costs an Organization
Unchecked lateral movement can transform an isolated endpoint incident into a much broader security event. By reaching additional systems, attackers gain more opportunities to steal credentials, access sensitive information, disable defenses, and prepare disruptive actions such as ransomware deployment.
This escalation is often what turns a compromise of one workstation into a network-wide ransomware incident or large-scale data breach. The impact grows with every additional endpoint, server, account, or application the attacker reaches.
Each affected system also increases the operational burden on incident responders. Security teams may need to determine when the system was accessed, which credentials were exposed, what processes executed, whether data was transferred, and what other devices communicated with it.
As the affected environment expands, so does the remediation effort. Teams may need to reset credentials, rebuild endpoints, review authentication logs, validate application access, restore systems, and monitor for persistence across multiple parts of the network.
The business consequences rise alongside the technical scope. Wider incidents can lead to longer service disruption, more complex recovery efforts, and higher investigation and remediation costs.
Large-scale data exposure can also increase regulatory and compliance risk. The number of affected systems, users, and records may influence notification requirements, reporting obligations, and the overall severity of the incident.
Containing lateral movement early therefore limits more than attacker access. It directly reduces the potential blast radius of the incident, narrowing the number of systems that security teams must investigate, recover, and account for.
What Is Endpoint Isolation and How Does It Work?
Endpoint isolation is a containment action that restricts a compromised device’s network access while typically preserving connectivity to the security management console. This prevents the endpoint from communicating with other systems or external attacker infrastructure during investigation and remediation.
When security teams isolate an endpoint, they effectively remove its ability to participate normally in the network. The device can no longer freely connect to peer endpoints, internal servers, shared resources, or internet-based command-and-control infrastructure.
At the same time, management connectivity is often preserved so responders can continue working with the affected system. Security teams can investigate alerts, review activity, collect evidence, and perform remediation without physically disconnecting the device or losing remote visibility.
This makes endpoint isolation particularly effective against lateral movement. An attacker may still have a malicious process running on the compromised endpoint, but that process loses the network path needed to reach additional devices or communicate with external infrastructure.
For defenders, this creates an immediate containment boundary around the affected system. Instead of relying solely on identifying every malicious action before it occurs, isolation restricts what the attacker can reach while the investigation continues.
In practical terms, endpoint isolation lateral movement controls reduce the attacker’s available network pathways, limiting the compromised endpoint’s ability to become a staging point for broader intrusion activity.
Device Quarantine Workflows: Isolate Risky Endpoints with Hexnode
Learn how device quarantine workflows contain endpoint threats and support faster, controlled incident response.
Isolation vs. Other Containment Actions
Endpoint isolation addresses a different layer of an attack than process termination or file quarantine.
Process termination stops a specific running process. File quarantine prevents a suspicious or malicious file from remaining accessible or executable. Endpoint isolation, by contrast, restricts the device’s network communications.
These controls therefore solve different containment problems. Terminating malware may stop its current execution, but it does not necessarily remove persistence or prevent another malicious process from starting. Quarantining a file does not address compromised credentials or attacker sessions already active on the endpoint.
Security teams often combine these actions during incident response. They may isolate the device to stop further network activity, terminate identified malicious processes, and quarantine malicious files while investigating persistence, credential exposure, and other indicators of compromise.
Isolation is therefore best treated as a network containment measure within a broader remediation workflow, not as a standalone fix.
Featured Resource
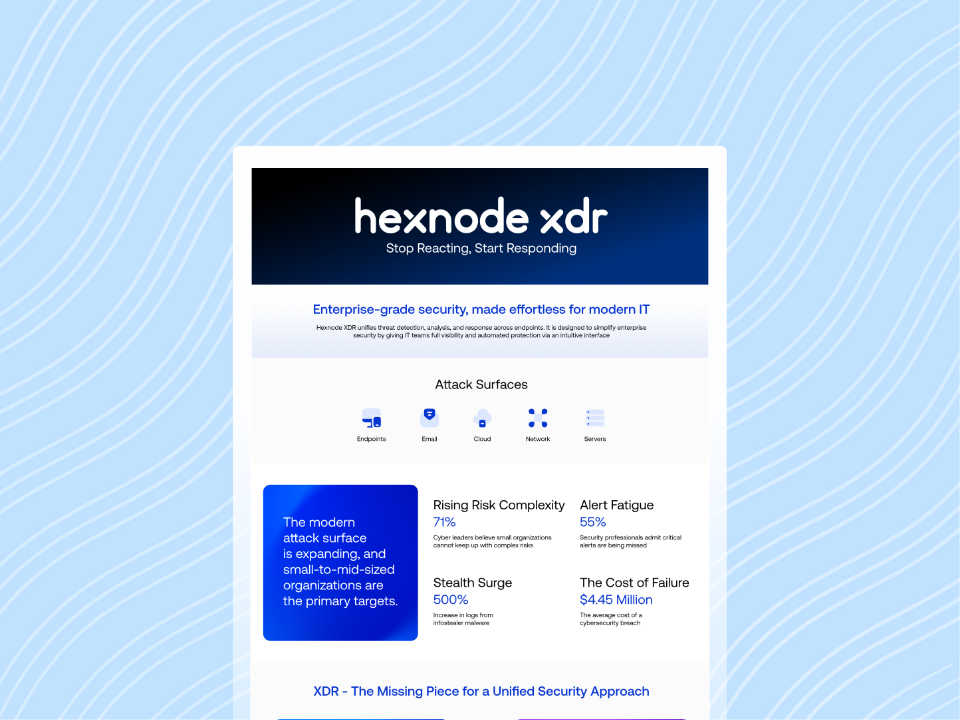
Hexnode XDR Info Sheet
Explore Hexnode XDR capabilities for threat detection, investigation, response, and stronger endpoint security.
Hexnode XDR provides an Endpoint Isolation capability designed to contain a compromised endpoint by disconnecting it from all networks while maintaining its live connection to the Hexnode XDR console for forensics. With a single action, security teams can cut the device off from network access while maintaining its connection to the Hexnode XDR console for continued investigation and forensic activity.
Isolation addresses the network dimension of an active compromise, but effective containment may require additional response actions. Hexnode XDR pairs device isolation with Kill Process and Quarantine File capabilities as part of its response toolkit. Administrators can terminate malicious processes and quarantine identified malicious files while keeping the affected endpoint separated from other systems.
This layered approach helps security teams respond to multiple components of the same incident. Device isolation restricts network communication, process termination stops identified malicious execution, and file quarantine contains malicious binaries stored on the endpoint.
After containment, administrators can execute a verification Deep Scan from the Hexnode console to assess device health and help verify the endpoint’s security state following remediation.
Together, these response actions support a controlled progression from containment to investigation and remediation, reducing the opportunity for a compromised endpoint to enable further lateral movement.
FAQs
When should security teams isolate a compromised endpoint?
Security teams should isolate an endpoint when continued network access could enable lateral movement or further attacker communication. Isolation is especially useful during active investigations because it limits network reach while responders examine and remediate the device.
What is the difference between endpoint isolation and file quarantine?
Endpoint isolation restricts a device’s network communications, while file quarantine contains a specific suspicious or malicious file. Security teams can use both actions together because they address different parts of an active compromise.
Does endpoint isolation remove malware from a compromised device?
No. Endpoint isolation contains network activity but does not automatically remove malware, persistence mechanisms or compromised credentials. Responders still need to investigate the endpoint, terminate malicious processes, quarantine relevant files and complete remediation.
Stop Lateral Movement Before It Starts
Fast endpoint isolation can be the difference between containing one compromised device and investigating an attack across an entire network. By cutting the affected endpoint off from other systems, security teams can restrict the attacker’s available paths while preserving access for investigation and remediation.
Hexnode XDR supports one-click Endpoint Isolation, disconnecting a compromised device from network access while maintaining its live connection to the XDR console for forensic investigation. This gives responders a practical way to contain endpoint isolation lateral movement without immediately losing visibility into the affected system.
For organizations evaluating stronger endpoint response capabilities, Hexnode offers a 14-day free trial. You can also request a demo to see how Hexnode XDR’s one-click isolation and coordinated response actions fit into your incident-response workflow.
Start your 14-day free trial or request a Hexnode XDR demo.
Stop Lateral Movement Faster
Isolate compromised endpoints, contain active threats, and accelerate incident response with Hexnode XDR.
Content writer at Hexnode. Fueled by good coffee and the occasional cat cuddle, I enjoy crafting content that informs, connects, and resonates. Nothing excites me more than knowing my words have been read, appreciated, and maybe even bookmarked.