Your IT environment is ready for an AI agent pilot when you can delegate a defined task, verify its outcome, and intervene when necessary. An AI agent’s IT readiness checklist helps you assess whether those foundations are in place.
For IT teams planning a first deployment, the gaps may sit in the workflow itself. Device records may be outdated, access permissions broader than the task requires, or troubleshooting procedures dependent on knowledge that has never been documented.
Before connecting an agent to a live workflow, identify which information it needs, what it can change, and who handles exceptions. IT administrators and directors need clear answers to these questions before deciding how much responsibility to delegate. Each unresolved gap should have an owner and a corrective action.
What can go wrong when IT introduces agents too early?
Introducing AI agents before the supporting controls are ready can increase operational errors and create more work for IT.
Incorrect changes: Incomplete context or unclear instructions may cause an agent to modify the wrong resource.
Unnecessary access: Excessive permissions can let an incorrect or manipulated request affect systems and data beyond the intended task.
Service interruptions: Changes made without checking dependencies may disrupt applications or user access, requiring manual recovery.
Additional investigation work: Missing action records and unclear ownership can make it harder to establish what happened and who should respond.
What does AI agent readiness mean in IT operations?
AI agent readiness is the operational ability to give an agent a bounded task, appropriate information and access, human oversight, and measurable acceptance criteria. These foundations determine what responsibility IT can safely delegate.
How do agents differ from fixed automation?
An LLM-based agent can select tools and take actions toward a goal, using context and tool results to determine what to do next. This extends beyond generating an answer for a person to act on.
A fixed automation follows predefined steps and conditions. An agent can choose among permitted actions as information becomes available, but the surrounding system must enforce its access and execution limits.
How much responsibility should IT delegate?
The appropriate level of delegation depends on the workflow:
Recommendations: The agent gathers information and proposes a response. A person evaluates the recommendation and performs any changes.
Actions requiring approval: The agent prepares an action, but execution requires an authorized person’s approval.
Actions within enforced limits: The agent performs predefined, permitted actions within restrictions on resources, scope, and execution.
AI Endpoint Management Glossary: Copilots, Agents, Automation, and Scripts Explained
Understand copilots, agents, automation, and scripts in AI endpoint management.
What should an AI agent’s IT readiness checklist include?
An AI agent’s IT readiness checklist should cover workflow scope, data, integrations, access permissions, human oversight, recovery, testing, and pilot boundaries. Assess each area against documented evidence, assign an accountable owner, and record unresolved gaps before deciding whether the proposed workflow can proceed.
Workflow scope and success criteria
Choose a limited task with an observable outcome. Document where the workflow starts, what the agent may do, and where its responsibility ends.
Define the task and its boundaries
Trigger and inputs: Specify what initiates the workflow and which information must be available.
Permitted work: List the actions the agent may perform, and the evidence needed to confirm completion.
Escalation conditions: Identify missing information, conflicting records, or requests outside scope that require technician review.
Baseline and suitability: Record current handling time and correction effort. Assess whether the task requires contextual interpretation or whether a conventional rule or script already meets the requirement.
Hypothetical example: An agent gathers device details and relevant ticket history, then proposes a troubleshooting action. Its task ends when it presents that recommendation with supporting context. The technician reviews the proposal and decides whether to make a change.
Data quality and approved use
Identify the information required for the selected task. Asset inventory, ownership records, ticket history, and runbooks need clear sources and assigned owners for maintenance.
Verify the information the agent will use
Check reliability: Use current records and consistent identifiers. Define authoritative sources and assign owners to correct gaps.
Review data handling: Confirm what providers receive, where they process it, retention periods, and reuse terms before sharing sensitive information.
Separate content from authority: Treat retrieved content as data, not permission to act. Enforce access controls independently of prompts.
Handle uncertainty explicitly: Pause when essential information is missing, outdated, or conflicting. Request clarification instead of filling gaps.
Integrations and access permissions
List every API, connector, and service identity the workflow needs. Confirm that each connection supports the required operation within the intended access scope.
Check connection scope and failure behavior
Supported operations: Verify available read and change operations, authentication, and connectivity.
Permission boundaries: Separate read and change permissions. Limit access to required resources and actions with least privilege access.
Credential control: Assign credential owners and verify that expiration or revocation blocks access.
Failure handling: Test outages, rejected requests, and interrupted connections. Define when to stop, limit retries or escalate.
Ownership and human oversight
Assign people who understand the workflow and have time to review its actions. Responsibilities should fit existing change management and incident processes.
Document approval and escalation responsibilities
Workflow owner: Assign accountability for scope, success criteria, exceptions, and continued use.
Operational reviewer: Give a qualified reviewer enough context and time to assess proposed changes.
Approval requirements: Define which actions need approval. Show the action, target, parameters, and expected impact before execution.
Escalation contact: Route rejected, delayed, or unanswered requests to a named contact. Silence is not approval.
Human handoff: Escalate unresolved, blocked, or out-of-scope tasks with a record of completed work and remaining uncertainties.
Activity logging and recovery
IT needs enough evidence to reconstruct a run and enough control to stop further actions. A submitted command alone does not establish that the intended change occurred.
Establish traceability and recovery controls
Record activity: Link requests, timestamps, tools, targets, approvals, and results. Exclude credentials and unnecessary sensitive data.
Verify outcomes: Check system state against completion criteria. Distinguish pending, failed, and partial actions from confirmed success.
Test interruption: Test stopping new actions, disabling access, and handing off work. Check operations already submitted.
Plan recovery: Define recovery for partial completion and identify irreversible actions. Stopping an agent does not undo completed changes.
Limit operation: Set runtime, retry, and resource limits. Assign a reviewer and intervention thresholds for failures or unusual activity.
Testing and evaluation
Evaluate representative requests in an isolated or tightly restricted environment before a live pilot. Tests should reflect the conditions the agent will encounter, including incomplete information and failed dependencies.
Measure behavior against acceptance criteria
Normal requests: Vary wording and context. Check record selection, scope boundaries, and expected results.
Ambiguous or stale inputs: Test unclear, outdated, and conflicting information. Confirm the agent requests clarification or escalates.
Control failures: Test denied permissions, missing approvals, malicious instructions, and interruptions. Verify unauthorized access is blocked and failures recorded.
Operational value: Compare accuracy, verified completion, escalation, correction effort, time, and cost against the existing workflow.
Acceptance thresholds: Define acceptable results before testing. Base deployment decisions on both successful and failed cases.
Pilot readiness and boundaries
Use the evidence collected for each area to decide whether a limited pilot can proceed. Choose one status per row and assign a named person to each owner role.
Record the pilot decision
Readiness area
Evidence required
Owner
Status
Workflow scope
Defined task and success criteria
Workflow owner
Ready / Needs work / Blocked
Data quality
Validated sources and approved use
Data owner
Ready / Needs work / Blocked
Integrations and permissions
Connection and access test results
Integration owner
Ready / Needs work / Blocked
Human oversight
Approval and escalation responsibilities
IT service owner
Ready / Needs work / Blocked
Logging and recovery
Execution records and recovery tests
Operations lead
Ready / Needs work / Blocked
Testing and evaluation
Results against acceptance criteria
Test lead
Ready / Needs work / Blocked
Resolve critical gaps: Delay live execution until permissions, approvals, logs, and recovery are verified. Assign fixes and review dates.
Bound the pilot: Define approved users or devices, actions, review dates, success criteria, and stop conditions. Evaluate blockers individually.
Where does Hexnode Synapse fit into agentic IT operations?
Hexnode Synapse is an agentic AI-based IT orchestration tool. It applies advanced reasoning to unstructured context, dynamically connects API actions across systems, and uses context-aware agents to resolve IT workflows with minimal human intervention.
Preparing for this approach starts with reliable information, defined permissions, accountable oversight, and verifiable outcomes. These foundations help IT teams assess which workflows are suitable for agent involvement, what responsibility they can delegate, and where human review remains necessary.
Featured resource
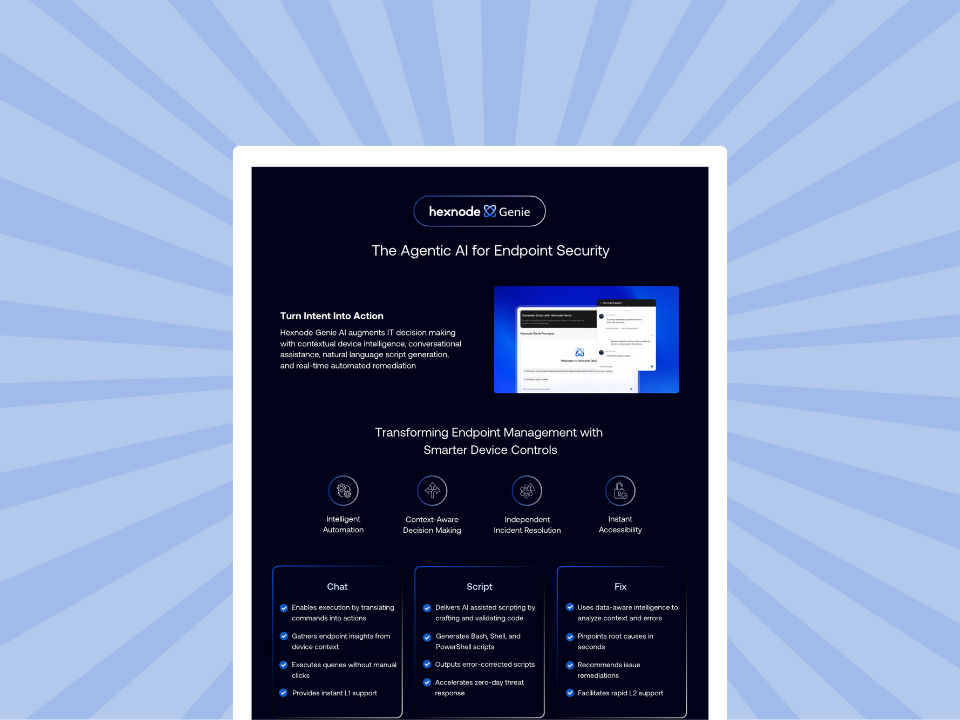
Hexnode Genie Info sheet
Explore how Hexnode Genie simplifies endpoint management with conversational assistance, contextual insights, and automated remediation.
Can we pilot an AI agent without allowing it to make changes?
Yes, you can limit the pilot to gathering information and recommending actions for technician review. Restrict access to the records needed for that task and keep change permissions disabled. Data handling, activity logging, and escalation controls still apply.
Do we need to replace existing scripts before introducing AI agents?
No, existing scripts can continue handling tasks with predictable steps and conditions. Consider an agent where the workflow requires interpreting context or choosing among permitted actions. Compare its results and review effort with the existing approach before expanding its role.
Does every data source need to be ready before an AI agent pilot?
Focus on the sources required for the selected workflow. Verify their freshness, consistency, ownership, and approved use, while keeping unrelated sources outside the pilot’s scope. Postpone tasks that depend on unresolved information gaps.
Prepare your IT workflows for agentic orchestration
Start with one suitable IT workflow and use the checklist to identify readiness gaps. Assign owners to unresolved issues and verify the required controls before introducing an agent into live operations. Set a review date, define success criteria, and agree on when to pause the pilot or return tasks to technicians. Learn more about Hexnode’s approach to agentic IT orchestration.
Ready to Introduce AI Agents?
Explore agentic IT orchestration with Hexnode Synapse.
A storyteller for practical people. Breaks down complicated topics into steps, trade-offs, and clear next actions—without the buzzword fog. Known to replace fluff with facts, sharpen the message, and keep things readable—politely.