Delayed patching prolongs vulnerability exposure and can lead to compromise, disruption, and emergency recovery work.
Visibility gaps, unclear ownership, compatibility concerns, and incomplete installations can delay fixes.
Assign owners, prioritize by risk, control deployment, manage exceptions, and verify that updates took effect.
Hexnode XDR supports investigation and containment, while Hexnode UEM handles supported patch deployment and reporting. Containment does not replace patching.
Known vulnerabilities can remain unresolved when security findings do not lead to completed, verified fixes. The risks of delayed patching persist when teams identify affected systems but cannot confirm that the required updates have taken effect.
SOC analysts identify exposures, IT operations manage deployment, and application owners assess compatibility. Without clear ownership and shared completion criteria, findings can stall between these responsibilities. A scheduled update or closed ticket may leave security teams without evidence that the vulnerability has been addressed.
The handoff needs to connect each finding with affected assets, a responsible owner, and a remediation deadline. Verified remediation also requires evidence that the fix was applied successfully and is effective on the affected systems.
What are the risks of delayed patching?
Delaying an applicable security patch prolongs exposure to the vulnerability it addresses. The consequences depend on exploitability, system exposure, privileges, and business importance. A missing patch does not automatically lead to a breach, but it can leave an available attack path open.
Compromise and data theft: Attackers may exploit an unpatched flaw to execute unauthorized code, access sensitive information, or gain additional privileges. What they can achieve depends on the vulnerability and the affected environment.
Ransomware-related disruption: Exploitable weaknesses can provide an entry point for ransomware, potentially interrupting services and access to business data. CISA recommends prioritizing patches for known exploited vulnerabilities, particularly on internet-facing systems.
Emergency recovery work: A resulting incident may require urgent containment, system restoration, and investigation. These activities divert security and IT staff from planned work and can extend operational disruption.
Repeated security investigations: Unresolved findings can trigger repeated triage and status checks, especially when analysts cannot distinguish outstanding exposure from outdated scan results.
Delays can also cause teams to miss internal remediation targets. During security reviews, incomplete installation records or stale assessments make it harder to establish which systems remain exposed, explain overdue fixes, and demonstrate whether approved exceptions are still justified.
What counts as delayed patching?
Delayed patching means postponing an available update for a system or application. It becomes a particular concern when deployment exceeds the organization’s risk-based remediation deadline.
The circumstances matter:
Planned testing: A documented testing period has a defined purpose, an accountable owner, and a completion date. It gives teams time to check compatibility before deployment.
Unmanaged delays: An overdue patch without an approved exception or a clear resolution plan leaves the exposure unresolved without an agreed path forward.
No available patch: When the vendor has not released a fix, teams need mitigation and continued review. This differs from postponing an available update.
Patch management includes identifying, prioritizing, installing, and verifying updates. A deployment request alone doesn’t confirm remediation; teams must verify the installation succeeded, and the update took effect.
The Ultimate Guide to XDR (Extended Detection and Response)
Understand XDR fundamentals, capabilities, comparisons, and implementation for security teams.
What causes organizations to delay security patches?
Security patches are delayed by gaps in asset visibility, unclear ownership, deployment constraints, and incomplete installations. Each can prevent an available fix from reaching affected systems and taking effect.
Incomplete inventories and unclear ownership
Missing software records make affected systems harder to identify. Disconnected deployment records and unclear application ownership can stall testing, approval, and follow-up.
Compatibility concerns and limited maintenance windows
Application dependencies, compatibility testing, and competing priorities can delay deployment. Necessary preparation needs a timeline and a review date to prevent indefinite postponement.
Unavailable endpoints and incomplete installations
Offline devices, failed installations, and pending restarts can leave updates incomplete. Teams must follow up to confirm that patches took effect.
Unsupported software without security fixes
When security fixes are no longer available, teams need an upgrade, replacement, or retirement plan, with temporary mitigations where appropriate.
How does XDR complement patch management?
Patch management applies software fixes, while Extended Detection and Response (XDR) supports investigation and response to suspicious activity. Before remediation is complete, XDR helps teams identify activity that may require immediate attention.
Investigate endpoint activity: Unusual process execution, unexpected file changes, and suspicious network connections can help analysts assess whether an exposed system shows signs of compromise.
Separate exposure from exploitation: A vulnerability finding does not prove that attackers have exploited it. Equally, an absence of alerts does not establish safety, particularly where monitoring coverage or telemetry is incomplete.
Coordinate response and remediation: Suspected compromise requires incident response alongside patching. Monitoring or containment does not remove the underlying software vulnerability. Installing a patch also does not prove that an existing intrusion has been eradicated; teams must investigate and address any remaining attacker access or malicious activity.
How can security and IT teams reduce patching delays?
Security and IT teams can reduce patching delays through clear ownership, risk-based priorities, controlled deployment, documented exceptions, and verified closure. A shared workflow should define who acts at each stage, when work must finish, and what evidence confirms completion.
Step 1: Identify affected assets and assign ownership
Start by establishing which systems need remediation and who can authorize, deploy, and validate the fix.
Build the asset record
Record the affected software and version, asset owner, business importance, and network exposure. Include the latest inventory or scan timestamp so teams can identify outdated findings and refresh them before making deployment decisions.
Define the handoff
Assign security teams to assess priority, endpoint operations to deploy updates, and application owners to validate compatibility. Name an owner responsible for coordinating these tasks and confirming closure.
Maintain one remediation record linking the vulnerability, affected assets, responsible owner, target date, and required closure evidence. This gives each team a shared reference for outstanding work.
Step 2: Prioritize patches using threat and business context
Prioritize patches using known exploitation, internet exposure, asset importance, and vulnerability severity. Use CISA’s Known Exploited Vulnerabilities catalog as an input when assessing affected systems. A CVSS Base score measures severity and should not determine risk by itself.
Situation
Priority decision
Required response
Known exploitation affecting an exposed asset
Prioritize urgent remediation
Use emergency approval procedures to apply the fix or a validated temporary mitigation.
A vulnerability on a system with limited exposure
Assess remaining risk and business impact
Assign a remediation target and schedule controlled deployment.
Signs of compromise on an affected endpoint
Activate incident response
Investigate and contain the activity while coordinating remediation.
Set organization-specific targets with security and business owners. Define which conditions trigger emergency escalation, such as exploitation affecting an internet-facing service. Reassess priorities when exposure or threat information changes; limited exposure does not make a vulnerability harmless.
Step 3: Test patches and automate controlled deployment
Use testing and staged deployment to address compatibility concerns while keeping remediation moving toward its deadline.
Validate representative systems
Obtain updates from trusted vendor sources and check authenticity where supported. Test a pilot group that represents affected operating systems, business applications, and dependencies. Confirm installation success, application functionality, and required restarts.
Define recovery options before expanding deployment. Where rollback is unavailable, consider validated backups, system restoration, or a replacement environment appropriate to the workload.
Automate approved rollout
Expand from the pilot to successive device groups, checking results before each stage. Use maintenance windows for routine updates and an accelerated approval path for urgent vulnerabilities.
Where supported, automate approved deployments, bounded retries, and status notifications. Keep offline devices, failed installations, and postponed restarts in a follow-up queue with an owner and next action. Escalate repeated failures for investigation instead of allowing retries to continue without review.
Step 4: Manage exceptions and reduce exposure
Document every patching exception with a reason, accountable owner, expiry date, and review trigger.
Reduce exposure: Restrict network access, disable the affected service, or apply another vulnerability-specific mitigation where appropriate.
Validate temporary controls: Confirm that restrictions work and monitor relevant activity. These measures do not justify postponing an available fix indefinitely.
Plan for unsupported systems: Set an upgrade, replacement, or migration date when security fixes are unavailable.
Review exceptions when threat information, system exposure, or business requirements change. Route evidence of exploitation into the incident-response process immediately, even if a patching exception remains approved.
Step 5: Verify remediation and review overdue work
Before closure, confirm the installed version, completion of any required restart, and an updated vulnerability assessment. Investigate stale results and partially completed deployments.
Track three remediation measures
Use a defined asset population, reporting cutoff, and consistent timestamps:
Overdue assets by risk tier: Count unique assets with findings past their target date within each tier.
Time to verified remediation: Measure each asset and vulnerability pair from first confirmed identification to verified closure.
Unresolved deployment failures: Count failed deployment tasks still awaiting successful retry or another resolution.
Address recurring delays
Review persistent failures and overdue work with their owners. Adjust approval processes, maintenance windows, or escalation criteria based on the causes.
Patch-status records support operational reviews; they do not independently establish legal compliance.
Featured resource
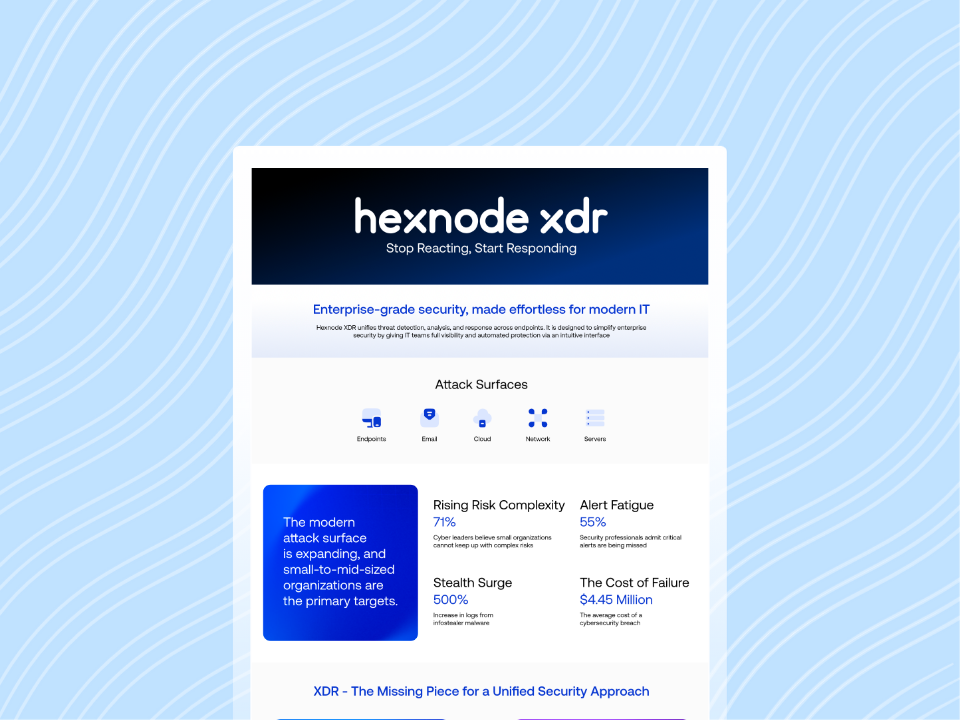
Hexnode XDR Info Sheet
Explore how Hexnode XDR unifies threat detection, investigation, and response for stronger enterprise endpoint security.
How does Hexnode support patch remediation and threat response?
Hexnode XDR supports threat investigation and containment, while Hexnode UEM handles supported patch deployments and update reporting.
Investigate and contain suspicious execution
When analysts identify suspicious execution on an exposed endpoint, Hexnode XDR’s Visual Process Tree helps them examine process relationships. Endpoint Isolation restricts network connectivity while retaining the XDR console connection. Kill Process Tree terminates a selected process and its child processes.
These actions support containment; they do not install patches or remove the underlying software vulnerability.
Target and control patch deployment
Hexnode UEM’s Auto Patch automation with CVE conditions targets applicable catalog patches associated with specified vulnerabilities. Deployment depends on platform support, device availability, and patch applicability. CVE filtering selects patches for remediation; it does not discover every vulnerability.
The Windows deployment workflow includes:
Require update approval: Deploy only updates approved by an administrator.
Maintenance-window controls: Schedule update actions within configured windows, with separate overrides for downloads, installations, and restarts.
Configure retries: Retry failed automation actions within defined attempt and delay limits.
Identify outstanding patching work
Hexnode UEM’s devices missing updates report identifies devices with missing updates and includes the Last Successful Scan field. Check that timestamp before relying on the reported status.
The Updates awaiting approval report identifies patches pending administrator approval. Use these reports to direct follow-up while separately confirming installation, required restarts, and remediation before closing the finding.
FAQs
Can a lower-severity vulnerability need patching before a critical one?
Yes, a lower-severity vulnerability may warrant earlier remediation if attackers are exploiting it and an important system is exposed. Prioritization should consider exploitation, accessibility, and business impact alongside the CVSS Base score.
When should a security patch bypass the normal maintenance window?
Use an emergency deployment process when waiting would leave an unacceptable exposure, such as known exploitation affecting an internet-facing system. Follow accelerated approval procedures, perform appropriate validation, and prepare recovery options before deployment.
Why does a vulnerability scan still flag a system after patching?
The finding may reflect outdated scan data, an incomplete installation, a pending restart, or another affected software component that remains unpatched. Check the installed version and deployment results, complete required restarts, and refresh the assessment before closing the finding.
Reduce patching gaps with Hexnode
Connect security investigations, patch deployment, and verification across your devices. Bring your team’s remediation priorities and device requirements to a walkthrough focused on coordinating responsibilities, addressing outstanding updates, and confirming that fixes have taken effect.
Request a Hexnode demo to explore coordinated threat response and patch management for your environment.
Reduce patching delays across your fleet
Coordinate patching and threat response. Start your free trial.
A storyteller for practical people. Breaks down complicated topics into steps, trade-offs, and clear next actions—without the buzzword fog. Known to replace fluff with facts, sharpen the message, and keep things readable—politely.