Web content filtering controls where users can browse, while an SWG adds broader web-traffic inspection and threat protection, with data-security capabilities varying by product and configuration.
Use content filtering for URL, domain, category, DNS, and acceptable-use enforcement on managed devices.
Consider an SWG when you need capabilities such as malware scanning, SSL/TLS inspection, DLP, or off-network protection with remote-user traffic routed through the gateway, and verify that the selected product supports those functions.
Hexnode UEM provides endpoint-enforced Web Content Filtering across supported platforms and can complement, but does not replace, a full SWG.
Secure Web Gateway vs Web Content Filtering: Why the Two Get Confused
IT teams are often asked to “secure web access” across office laptops, remote endpoints and mobile devices. The problem is that vendors frequently use secure web gateway and web content filtering in overlapping ways, even though the two controls address different layers of web security.
Both technologies can restrict access to websites. However, web content filtering primarily determines which sites or categories users can reach, while a secure web gateway can apply broader security controls to web traffic, including threat inspection and data protection.
Web access can expose users to malicious sites, credential-harvesting pages and malware, while phishing may reach users through email, messaging, voice or web-based lures. Verizon’s 2026 DBIR found that Social Engineering represented 16% of breaches, while phishing appeared in 16% of breaches.
This guide explains how each approach works, compares their capabilities side by side and helps IT teams decide which controls fit their managed device fleet.
What Is a Secure Web Gateway?
A secure web gateway (SWG) is a security control positioned between users and the internet that inspects user-initiated web traffic and enforces security policies as that traffic passes between endpoints and internet destinations. Gartner defines an SWG as a solution that filters unwanted software or malware from user-initiated web traffic while enforcing corporate and regulatory policies.
SWGs commonly provide URL filtering and anti-malware controls, while capabilities such as application control, SSL/TLS inspection and DLP vary by product and configuration. SSL/TLS inspection decrypts encrypted web traffic so security controls can examine it before re-encrypting and forwarding it. DLP applies policies designed to prevent sensitive information from leaving the organization through web channels.
Organizations can deploy SWGs in several ways:
On-premises: Traffic passes through physical or virtual gateway infrastructure.
Cloud-delivered: Users connect to a provider’s distributed security service.
Hybrid: On-premises and cloud controls work together across different locations and device groups.
SWG is also a core security capability within Security Service Edge (SSE). Gartner defines SSE as primarily cloud-delivered security for access to the web, cloud services and private applications. Security Service Edge (SSE) is the security-services subset of SASE, while SASE converges those security capabilities with networking functions such as SD-WAN.
What Is Web Content Filtering?
Web content filtering is a policy control that allows or blocks access to websites based on URLs, domains, or content classifications. Organizations use it to enforce acceptable use policies, reduce exposure to malicious websites, and support compliance requirements without necessarily inspecting the contents of web traffic.
Common filtering methods include:
Blocklist filtering: Denies access to specific URLs or domains while allowing other destinations.
Allowlist filtering: Permits access only to approved websites and blocks everything else by default.
Category-based filtering: Restricts groups of websites based on classifications such as gambling, adult content, social media, or known malicious sites.
DNS-based filtering: Blocks connections by preventing devices from resolving prohibited or malicious domains.
CIS Controls v8.1 Safeguard 9.2 recommends DNS filtering on all end-user devices, including remote and on-premises assets, while Safeguard 9.3 calls for network-based URL filtering across enterprise assets using approaches such as category-based, reputation-based and blocklist filtering.
Featured resource
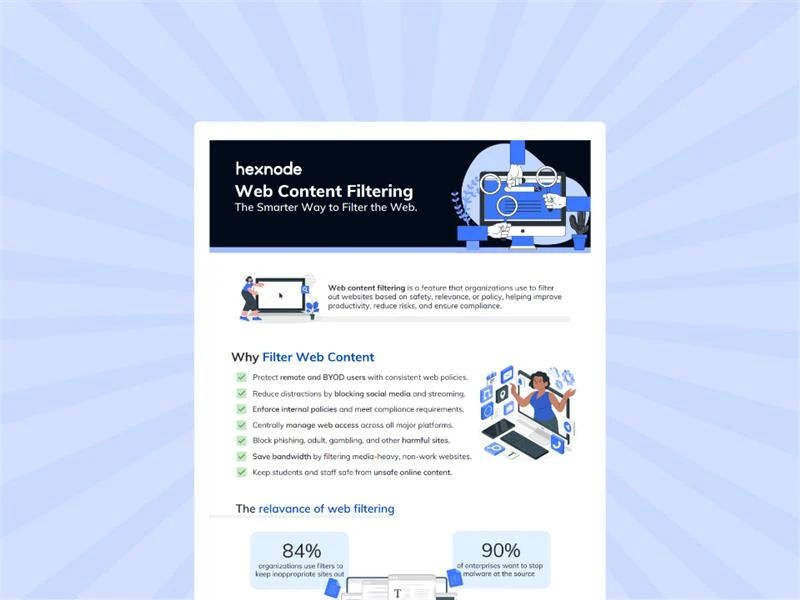
What Is Web Content Filtering?
Get a quick visual walkthrough of how web content filtering controls website access on managed devices.
Secure Web Gateway vs Web Content Filtering: Key Differences
A secure web gateway (SWG) inspects and controls user-initiated web traffic, combining access controls with threat-protection capabilities and, depending on the product, additional data-protection functions. Web content filtering has a narrower role: it determines which websites or categories users can access.
Criteria
Secure Web Gateway
Web Content Filtering
Core function
Inspects web traffic and enforces security policies
Allows or blocks websites and categories
Traffic inspection
Commonly supports malware scanning; TLS inspection and DLP vary by product
Usually does not inspect traffic content deeply
Where it is enforced
Network edge, cloud service or security proxy
Endpoint, DNS layer, browser or network
Remote-user coverage
Can inspect remote-user traffic when it is routed through the SWG
Depends on endpoint or cloud-based enforcement
Deployment complexity
Varies by deployment model, traffic-steering requirements and inspection depth
Varies by filtering method and enforcement model
Typical cost profile
Varies by vendor, deployment model, licensing and enabled capabilities.
Varies by vendor, licensing model and filtering capabilities
Best fit
Organizations needing web threat and data protection
Organizations needing access and acceptable-use controls
Web and URL filtering are core SWG capabilities, but standalone filtering controls can also operate independently at the DNS, endpoint, browser or network layer. SWGs commonly combine URL filtering and anti-malware controls, with some products also providing application control, HTTPS inspection and DLP. Some standalone filtering products, however, provide URL, category or DNS-based enforcement without inspecting web traffic for malware or sensitive data.
The practical decision is whether the organization only needs to control where users can browse, or whether it also needs to inspect what passes through those web sessions.
Which Do You Need: SWG, Web Content Filtering, or Both?
Choose web content filtering when the main requirement is controlling which websites managed users can access. Consider an SWG when the organization also needs deeper traffic inspection, malware protection, SSL/TLS inspection, DLP, or off-network inspection, and confirm that the selected SWG provides those capabilities.
Use these criteria to decide:
Fleet size and OS mix: For a smaller, tightly managed fleet, endpoint filtering may be enough. Larger, heterogeneous fleets may benefit from adding an SWG for centralized inspection.
Remote or hybrid workforce: If users frequently work outside the corporate network, consider a cloud-delivered SWG that can apply consistent web-security controls when their traffic is routed through the service.
Compliance obligations: If requirements focus mainly on acceptable-use restrictions, filtering may suffice. Regulations requiring stronger monitoring or data controls can justify an SWG.
Data-leak risk: Filtering can block risky destinations. Consider an SWG with verified DLP capabilities when sensitive data must also be inspected or prevented from leaving through web traffic.
Security resources: Organizations with limited staff may prefer simpler endpoint filtering. Teams equipped to manage traffic inspection and policy tuning can make fuller use of an SWG.
Budget: Compare licensing, deployment and operational costs for the specific products under consideration. Broader SWG capabilities may justify additional investment when threat inspection and data protection are required.
NIST SP 800-207 states that trust should not be granted solely because a user or device is inside the enterprise network. While organizations may layer device-level and traffic-level controls, NIST does not prescribe a specific combination of web content filtering and secure web gateways.
How UEM and Security Solutions Control Web Apps and Browser Security
Explore how endpoint, browser, and web-app controls work together to improve visibility and enforce secure access.
How Hexnode UEM Enforces Web Content Filtering on Managed Devices
The Web Content Filtering policy in Hexnode UEM applies web-access restrictions directly to managed endpoints. This makes it an endpoint-enforced filtering layer rather than an inline secure web gateway that inspects web traffic for malware, sensitive data, or encrypted threats.
Platform support differs:
Windows: Admins can configure blocklist or allowlist mode under Windows > Security > Web Content Filtering. The policy supports Microsoft Edge, Google Chrome, and Mozilla Firefox on Windows 10 and 11 Pro, Enterprise, and Education editions. Filtering is strictly URL-based; Hexnode does not provide a category-based filtering engine on Windows. Brave and Opera are not supported.
iOS: Web Content Filtering works on supervised iOS devices running iOS 7.0 or later. Admins can blocklist or allowlist URLs and enable Apple’s built-in Restrict Inappropriate Content filter.
Linux: Admins can manually add blocked or allowed websites or import URL lists through a CSV file.
macOS: Hexnode’s native Blocklist/Allowlist policy restricts URLs in Safari. Blocklist by Content automatically restricts explicit content and is enabled by default. Other browsers are not covered by this native policy.
Is web content filtering enough for a remote or hybrid workforce?
Web content filtering can be enough when the primary goal is controlling which websites managed users can access. If remote users also require malware scanning, SSL/TLS inspection, DLP, or broader traffic inspection, an SWG may be needed.
Can web content filtering inspect encrypted HTTPS traffic?
Basic web content filtering usually controls destinations rather than deeply inspecting traffic content. An SWG can add capabilities such as SSL/TLS inspection, malware scanning, and DLP to examine and control web sessions more extensively.
Does Hexnode UEM support category-based web filtering on Windows?
No. Hexnode UEM’s Windows Web Content Filtering policy is URL-based and supports blocklist or allowlist modes, but it does not provide a category-based filtering engine on Windows.
Does Hexnode UEM replace a secure web gateway?
No. Hexnode UEM provides endpoint-enforced web content filtering, while the draft identifies no verified native Hexnode capability for SWG-style SSL/TLS inspection, DLP, or cloud-proxy traffic inspection. It can therefore complement broader gateway controls rather than replace a full SWG.
Put the Right Web Access Controls on Your Device Fleet
Use web content filtering when the goal is to control which sites managed users can access, and consider an SWG when you also need deeper traffic inspection or additional threat and data-security capabilities supported by the selected product.
For teams evaluating endpoint-enforced filtering, seeing the policy workflow in practice can make the fit much easier to assess.
I write at the intersection of technology, process, and people, focusing on explaining complex products with clarity. I break down tools, systems, and workflows without any noise, jargon, or the hype.