


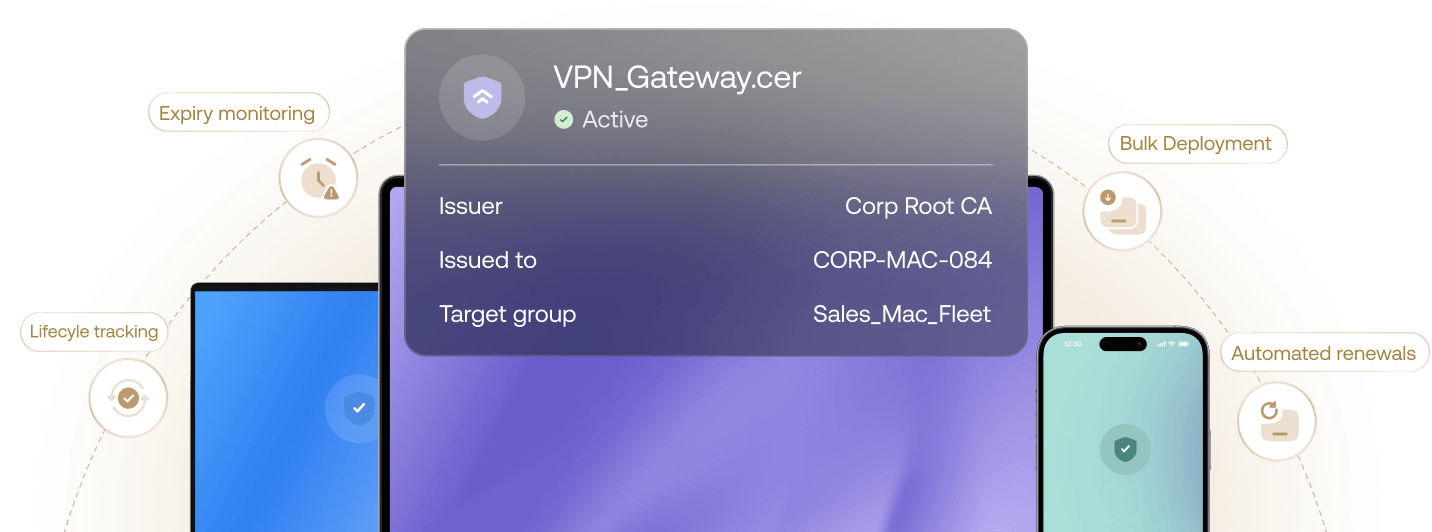
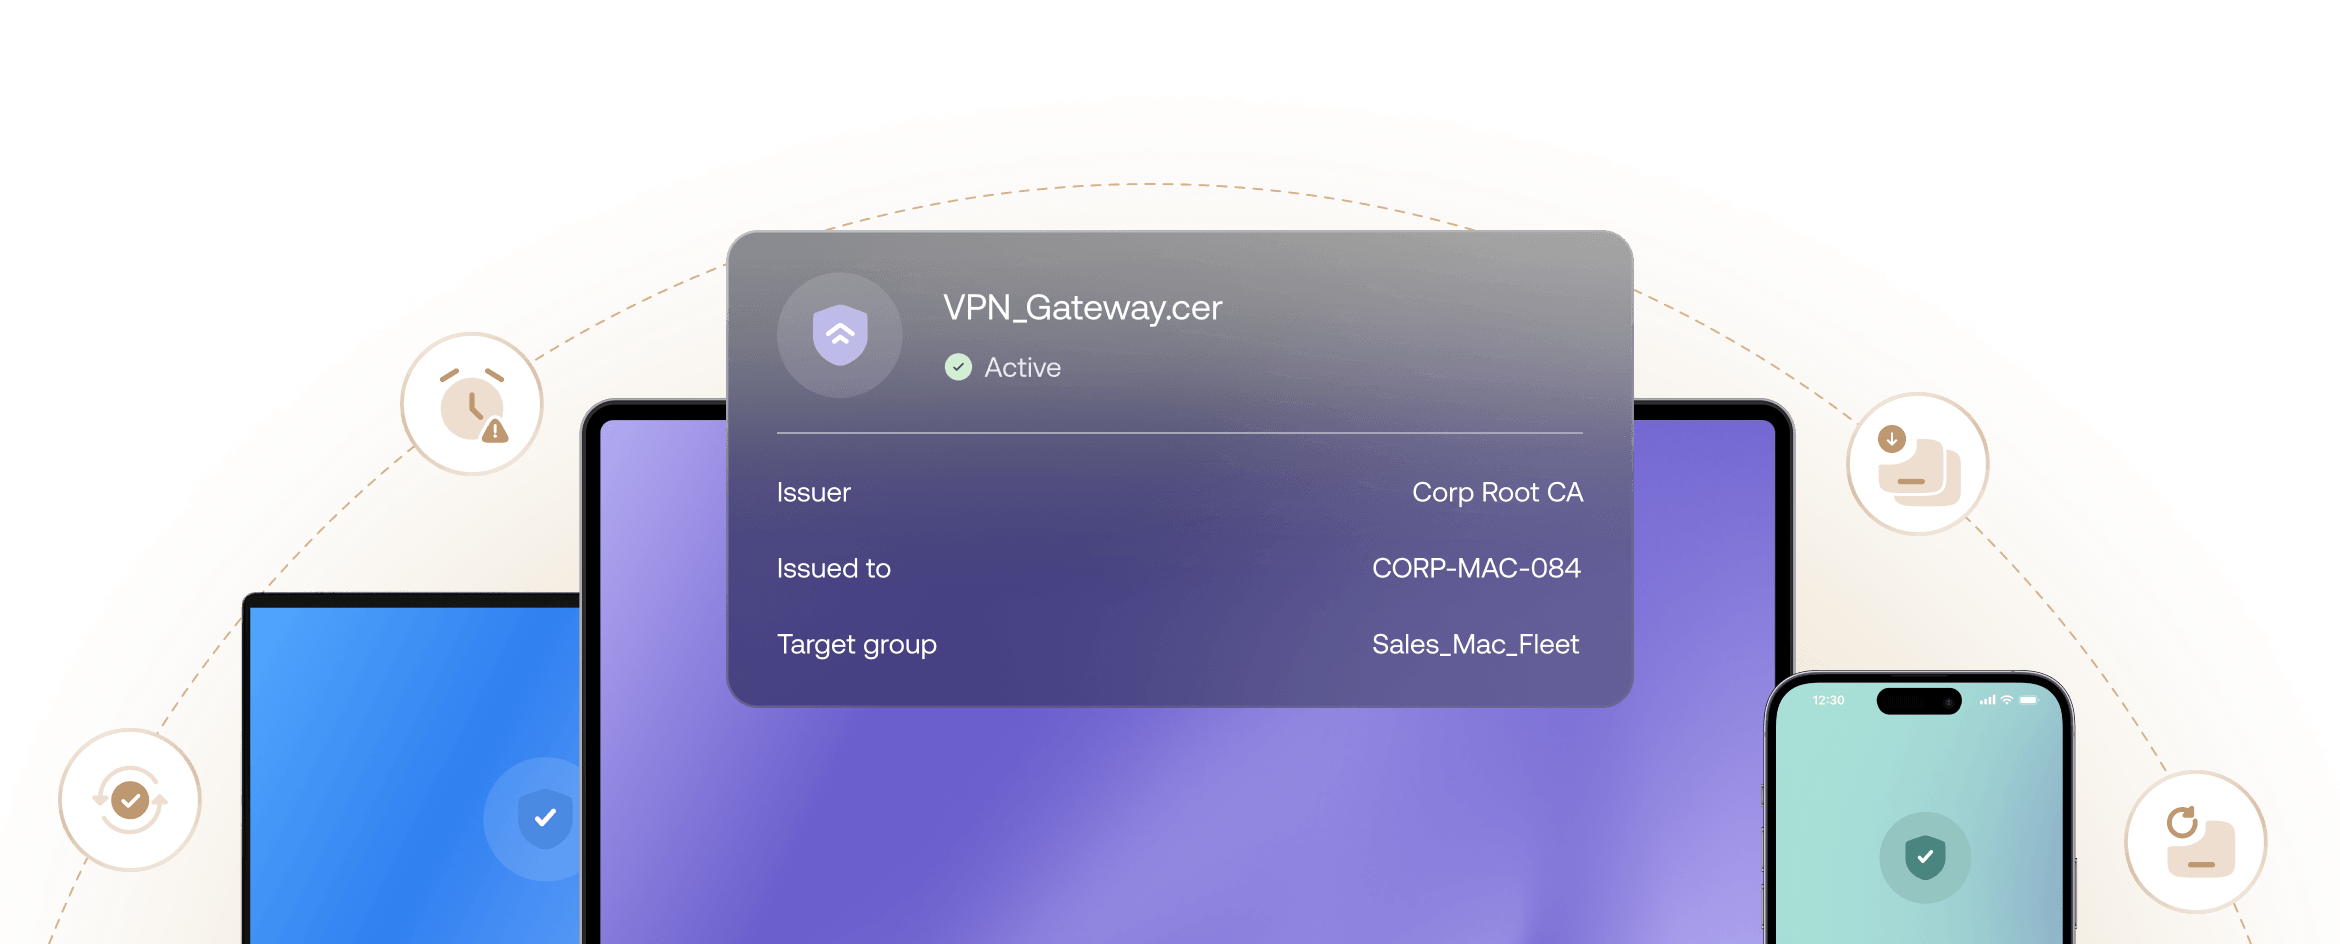
 Lifecyle trackingExpiry monitoringBulk DeploymentAutomated renewals
Loved by all. Recognized by the best.


Continuous Trust. Effortless Control.
Cross-Platform Provisioning
Standardize endpoint authentication across your fleet by natively provisioning 802.1X, VPN & S/MIME certs into Windows stores & Apple Keychain.
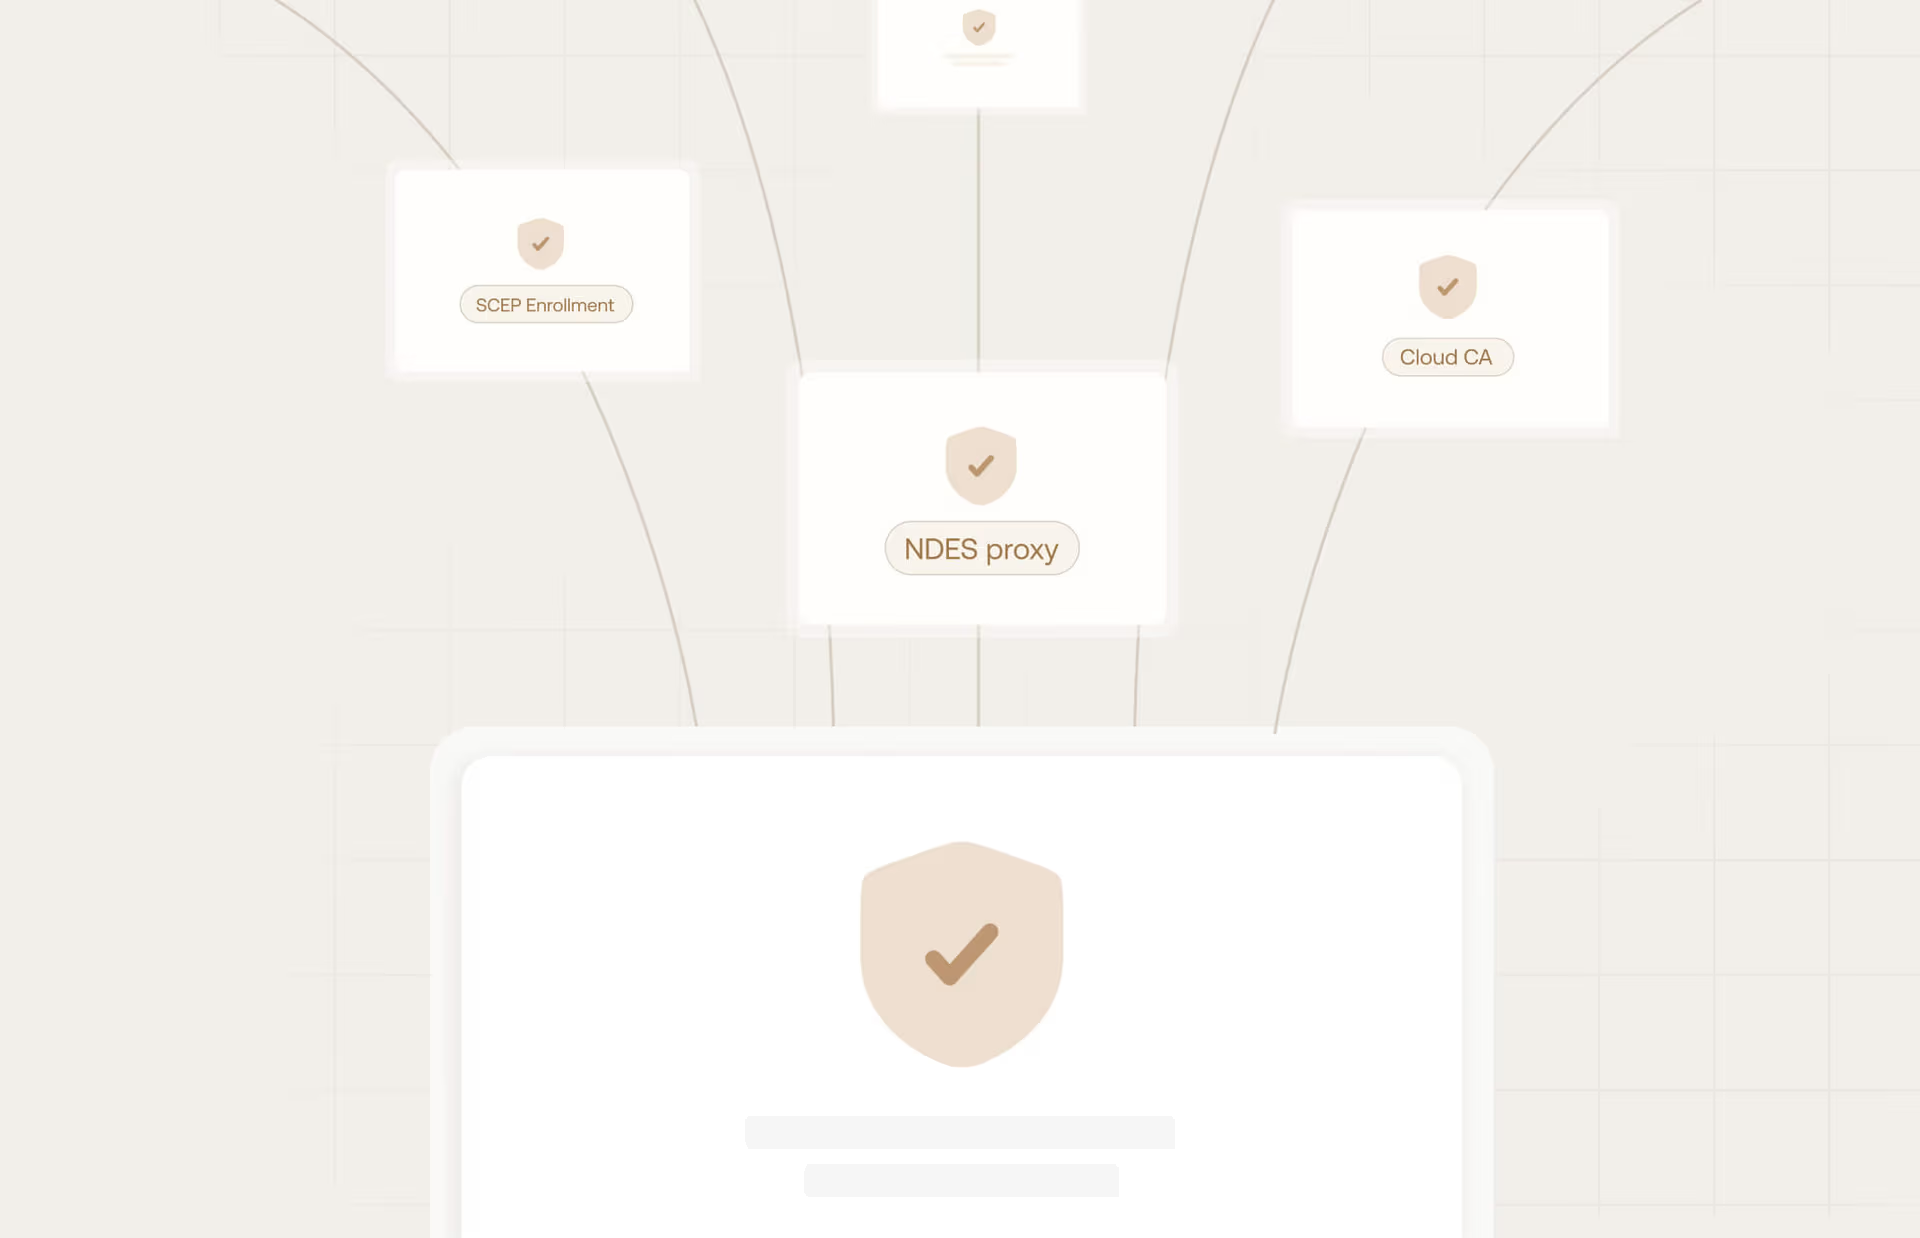
Scalable PKI Infrastructure
Deploy certificates at scale via NDES proxy or direct cloud CA integrations, ensuring every enrollment request is gated by dynamic SCEP validation.
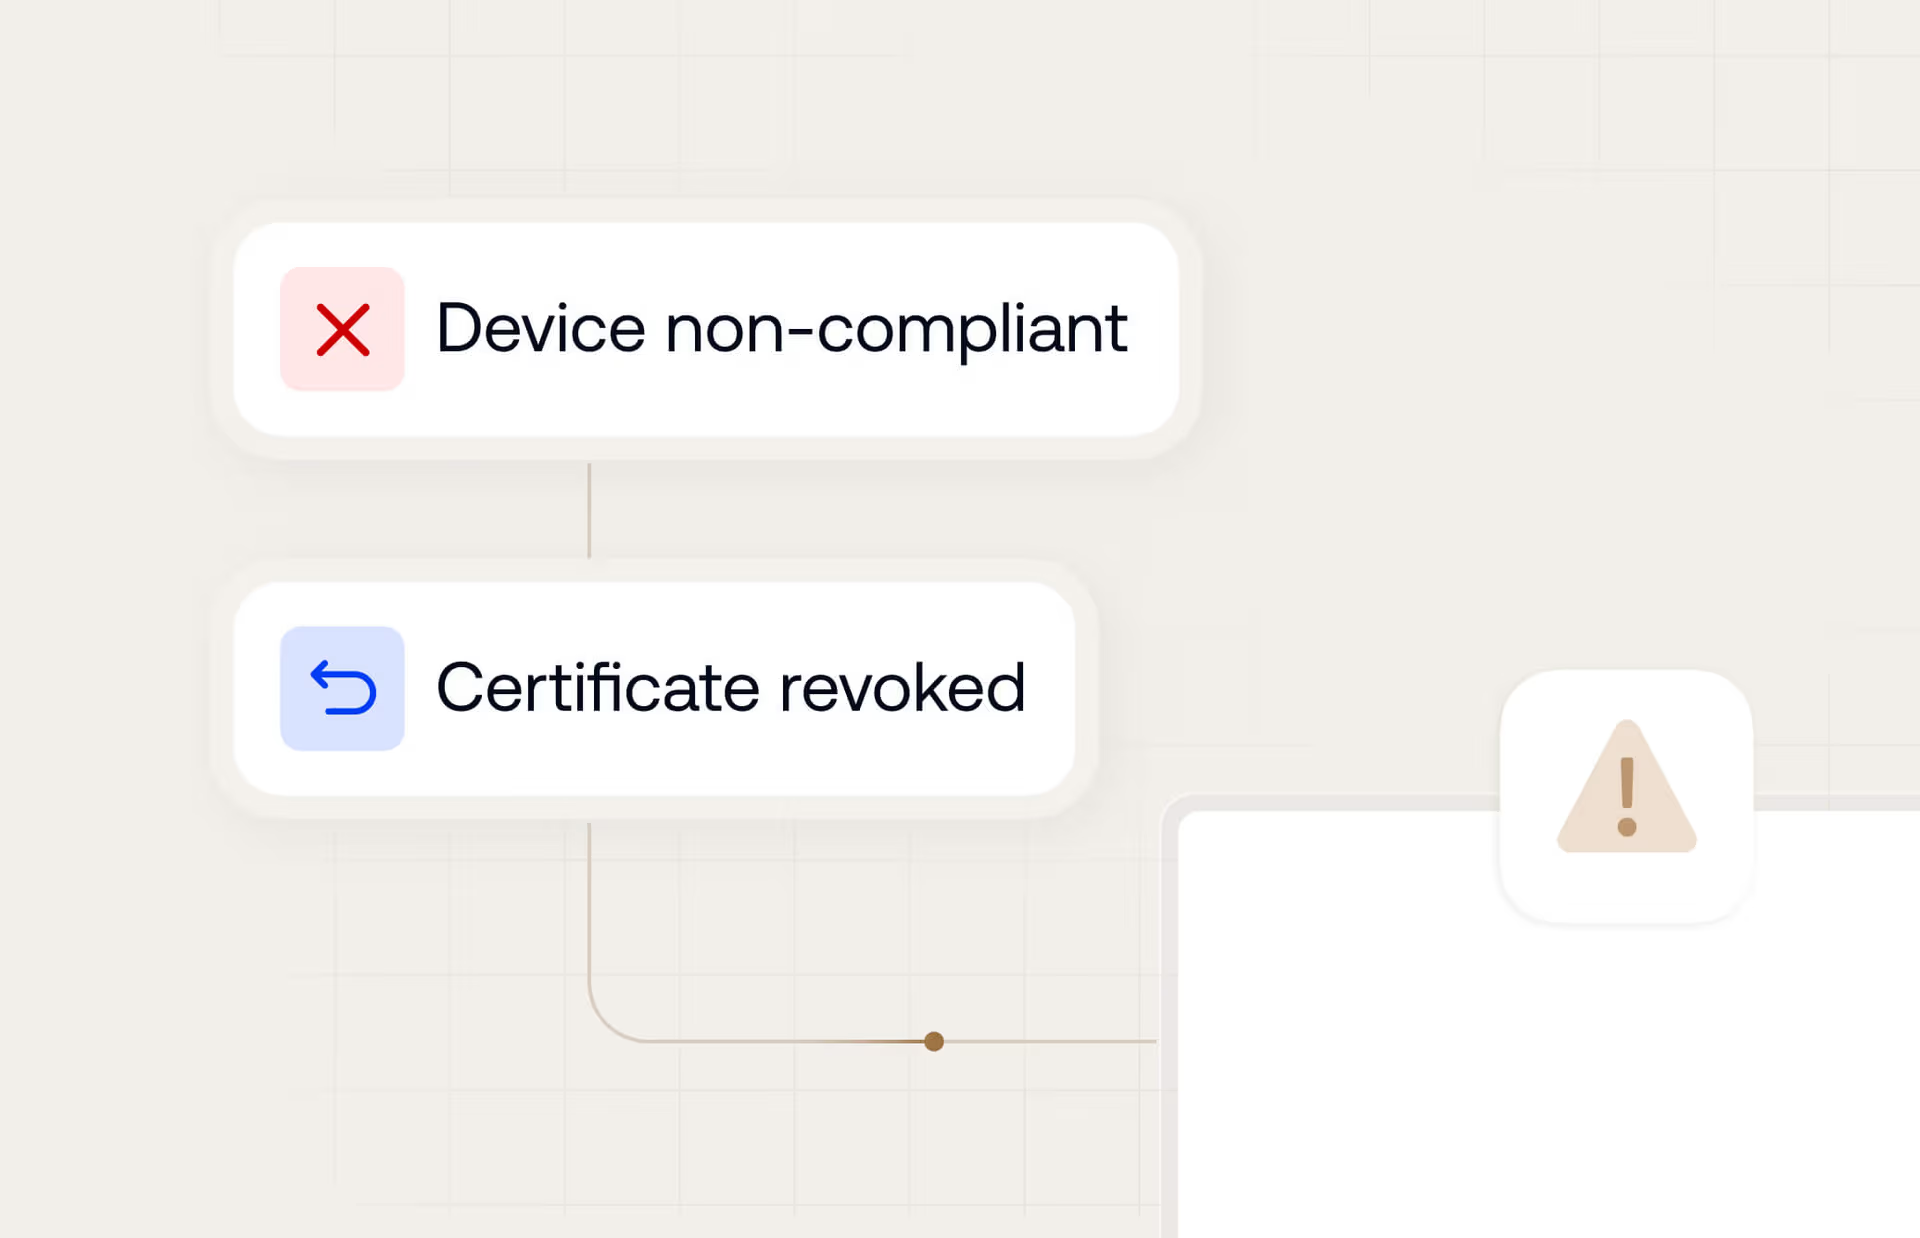
Status Driven Revocation
Instantly secure your perimeter by automatically revoking certificates via CRL/OCSP the moment a device is flagged as lost or non-compliant.
Comprehensive Certificate Support
Network Authentication Certificates
- Wi-Fi Certificates (802.1X)
- Always-On VPN Certificates
Secure Communication Certificates
- S/MIME Email Certificates
Identity & Device Validation Certificates
- SCEP / Client Identity Certificates
Trust Infrastructure Certificates
- Trusted Root Certificates (Root CAs)
- Intermediate Certificates


Autonomous Device Trust for Uninterrupted Security
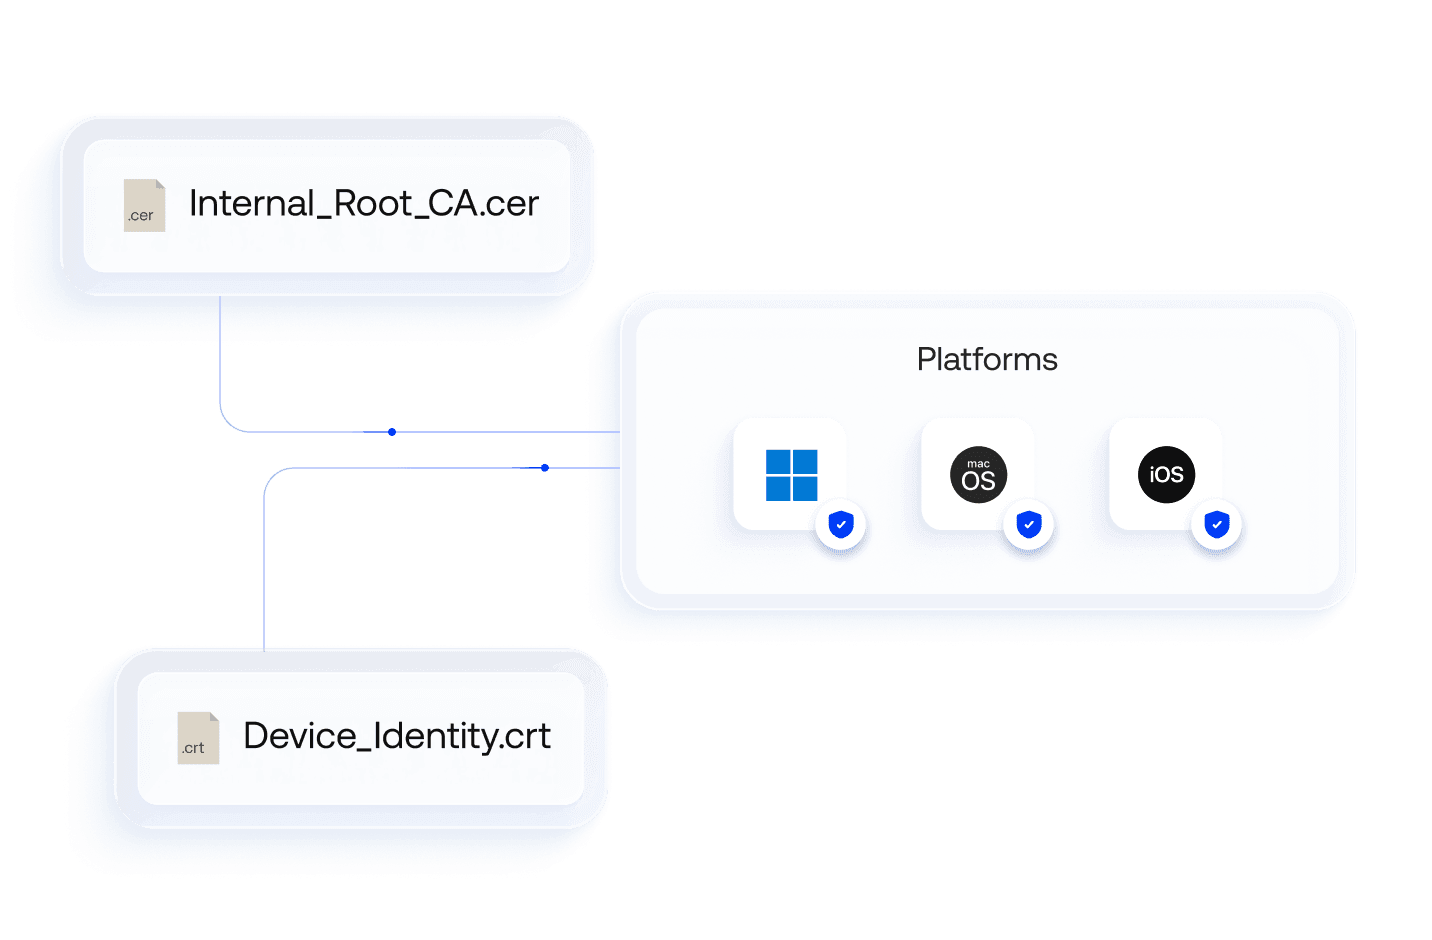
Root certificate deployment
Achieve seamless Zero Trust security and passwordless authentication across your fleet through automated root certificate deployment to all OS stores.
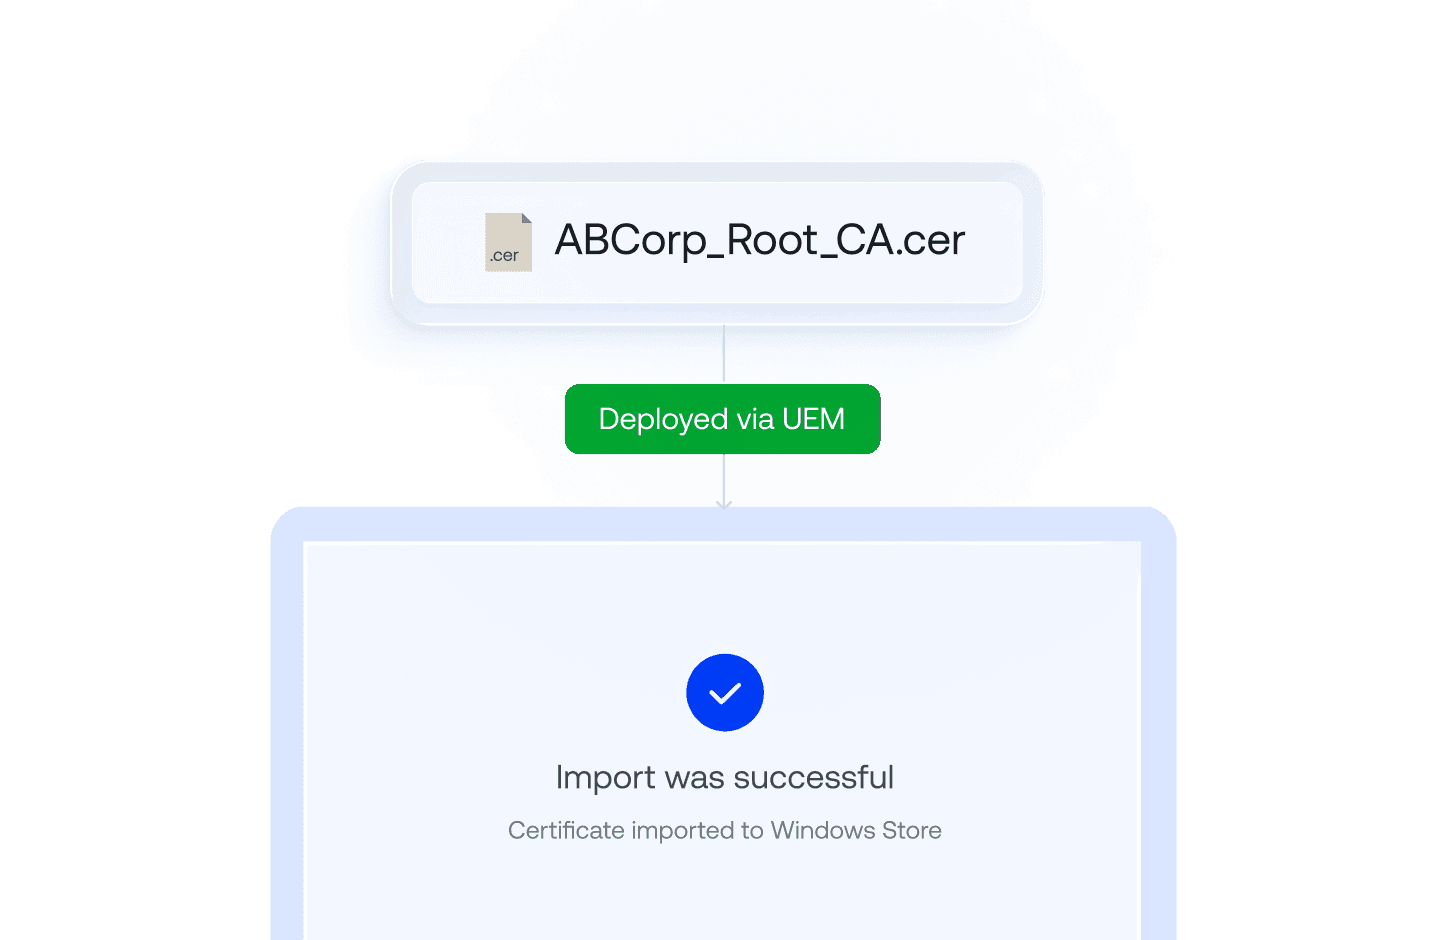
Windows Store Mapping
Ditch clunky GPOs and brittle PowerShell scripts by natively injecting certificates into Windows certificate stores via clean UEM commands.
Always on VPN Profiles
Protect data-in-transit across remote operations by deploying certificates that force an encrypted VPN tunnel the moment a device boots with zero user prompts.
S/MIME Email Security
Maintain cryptographic authenticity and privacy of corporate emails by provisioning user-specific certificates for native, client-side email signing and encryption.
.cer & .crt File Support
Simplify public key distribution through out-of-the-box parsing, validation, and deployment of universally accepted enterprise certificate extensions like .cer and .crt.
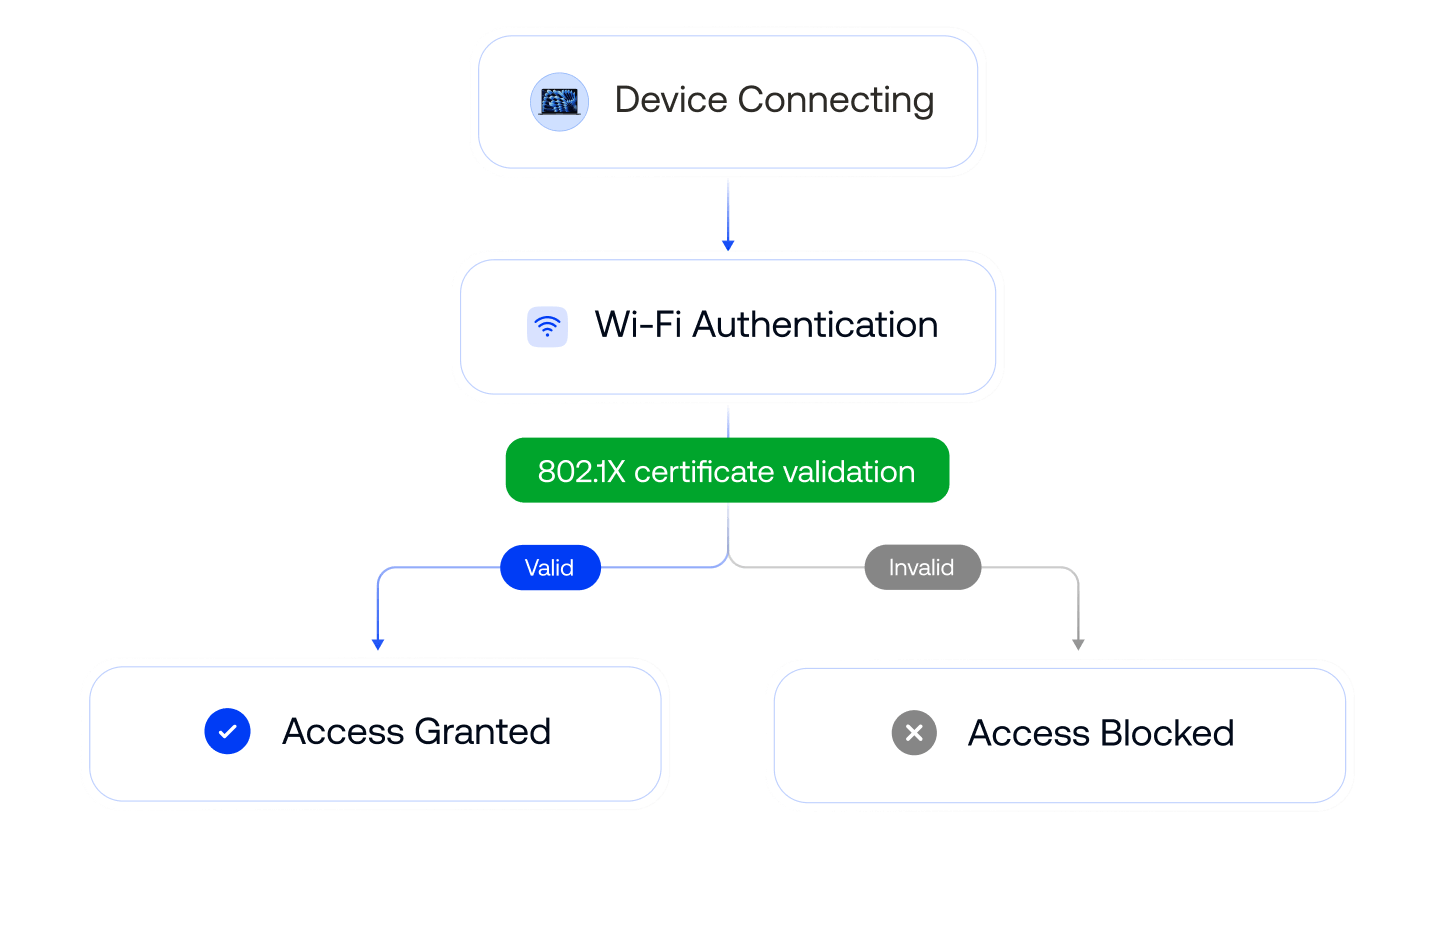
802.1X Wi-Fi Authentication
Eliminate rogue Wi-Fi access and credential sharing by deploying unique .cer or .crt certificates to validate unshareable, hardware-tied device identities.
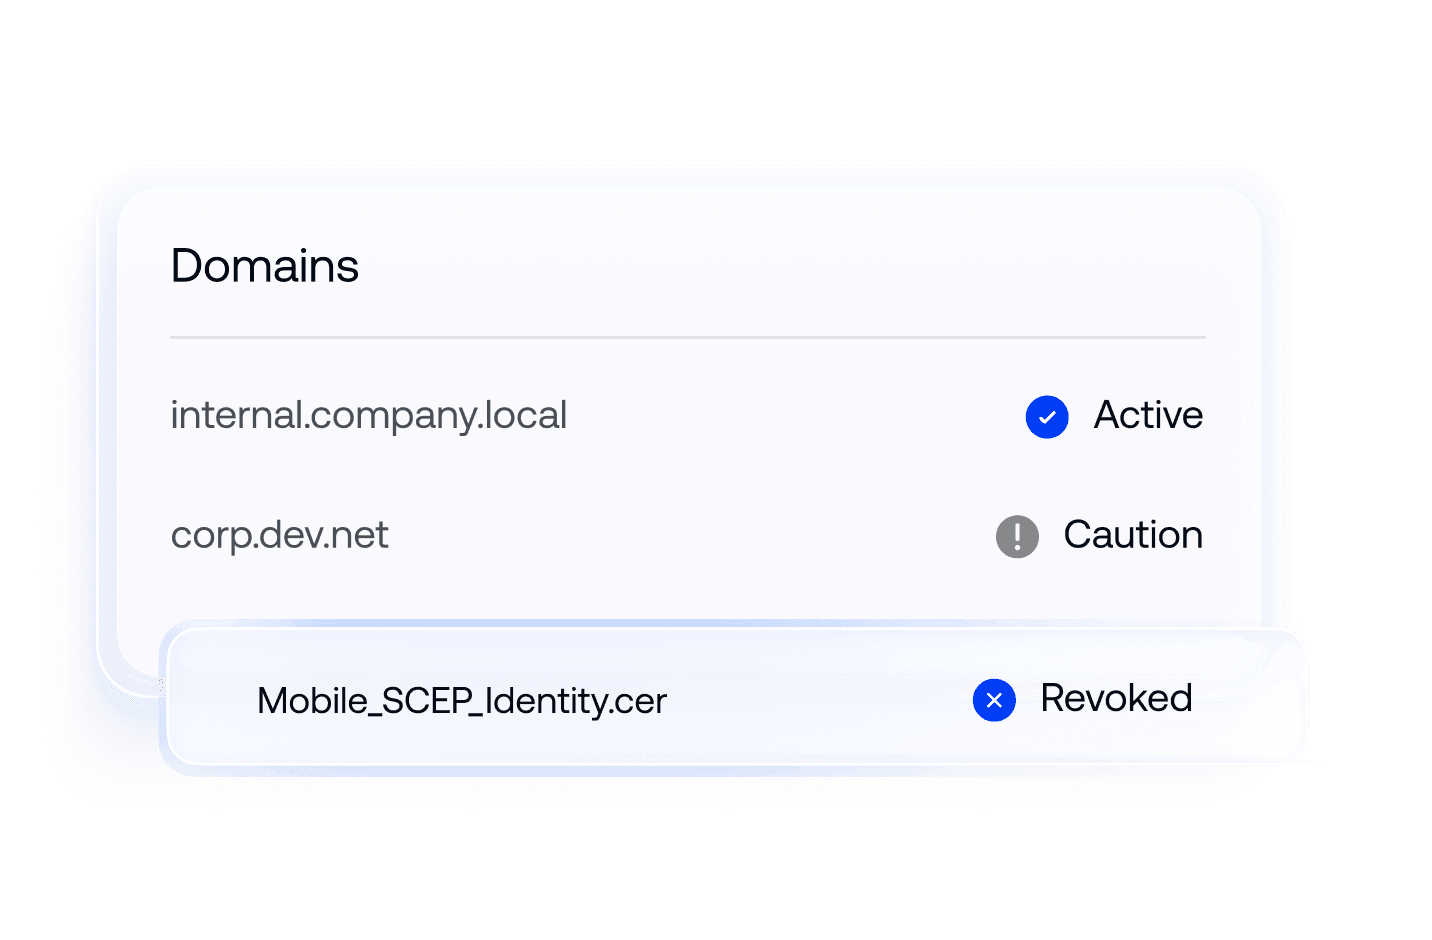
Apple CT Scan Exclusions
Simplify certificate-based authentication for Apple devices by managing certificate transparency, revocation, and trust preferences for macOS and iOS devices using a single policy.


Frictionless connections for a secure network

On-Premises CA Integration (AD CS)
Maintain device trust continuity by connecting cloud UEM to firewalled Microsoft AD CS servers via an outbound proxy and NDES/SCEP.

Cloud CA provider integration
Issue and deploy credentials at scale from preferred cloud trust providers via native APIs to automate certificate issuance the moment an endpoint enrolls.

IdP integration
Bind certificates to verified identities via Entra ID, Okta, and Google Workspace integrations to populate with user attributes and authorize CSRs.
See why enterprises around the world chose Hexnode

"By using Hexnode, the productivity and time savings have been very big. The time spent actually deploying a device has gone down. It used to take us about 20 minutes now it just takes us about 10."
Technology Solution Specialist
... and then we found Hexnode and it checked all of the boxes
Information Technology Manager,







14 day free trial
No credit card